
Monitor every control. Catch every gap before the next audit.
Secfix replaces manual compliance checks with 250+ automated tests that run continuously across your systems, people, devices, and vendors, for ISO 27001, SOC 2, ISO 42001, GDPR and more.



Stop chasing compliance once a year
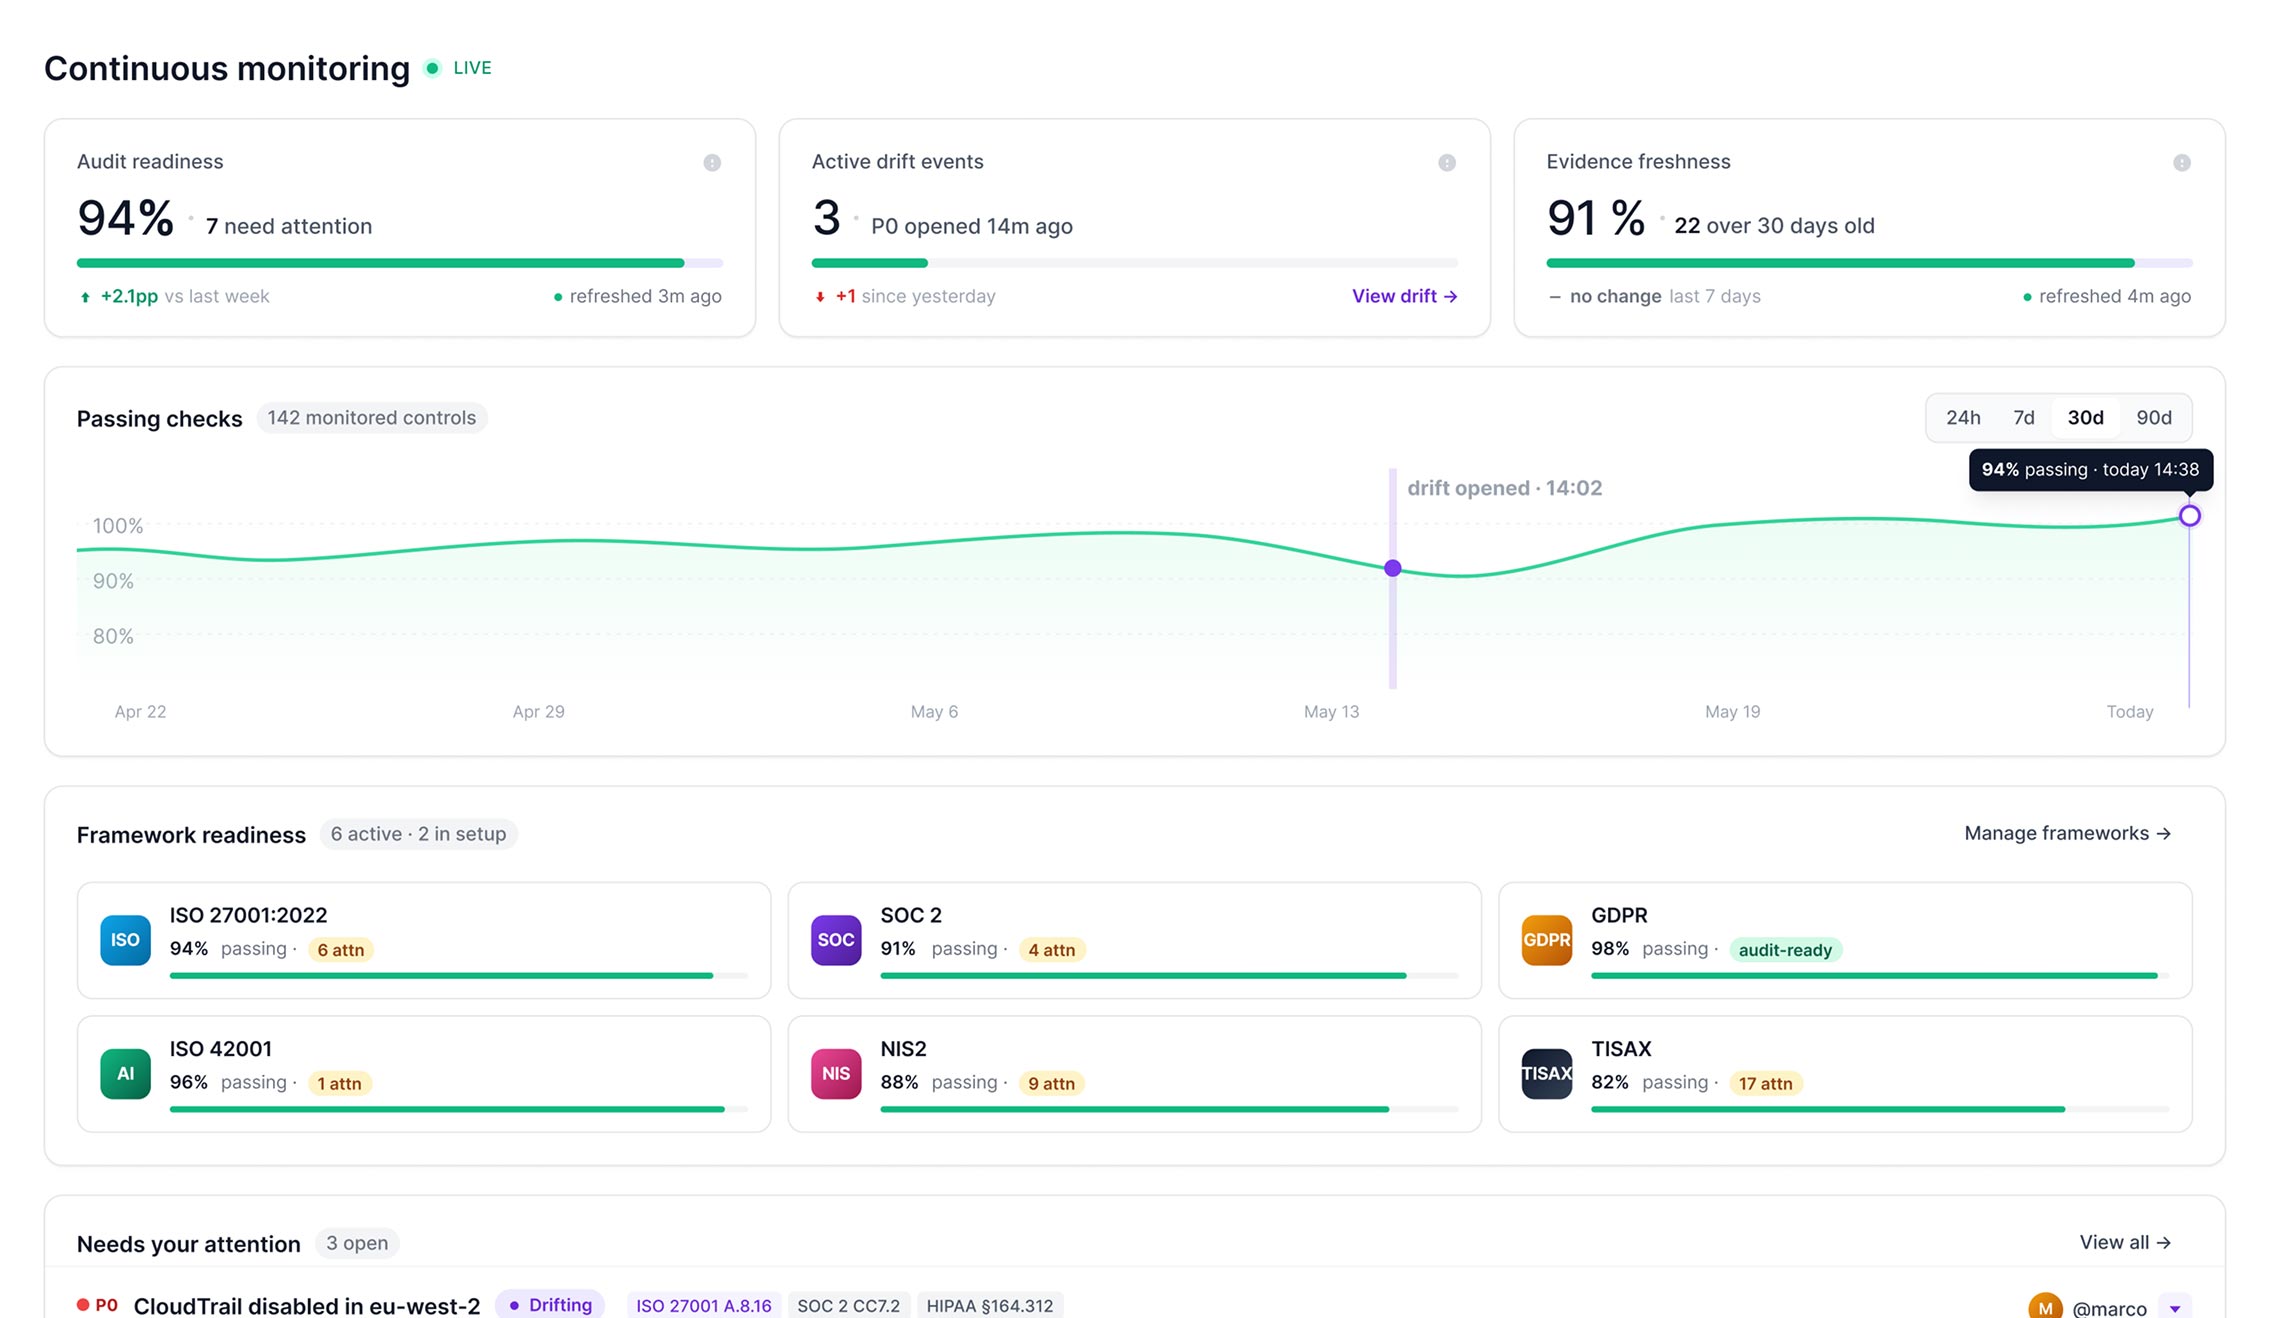
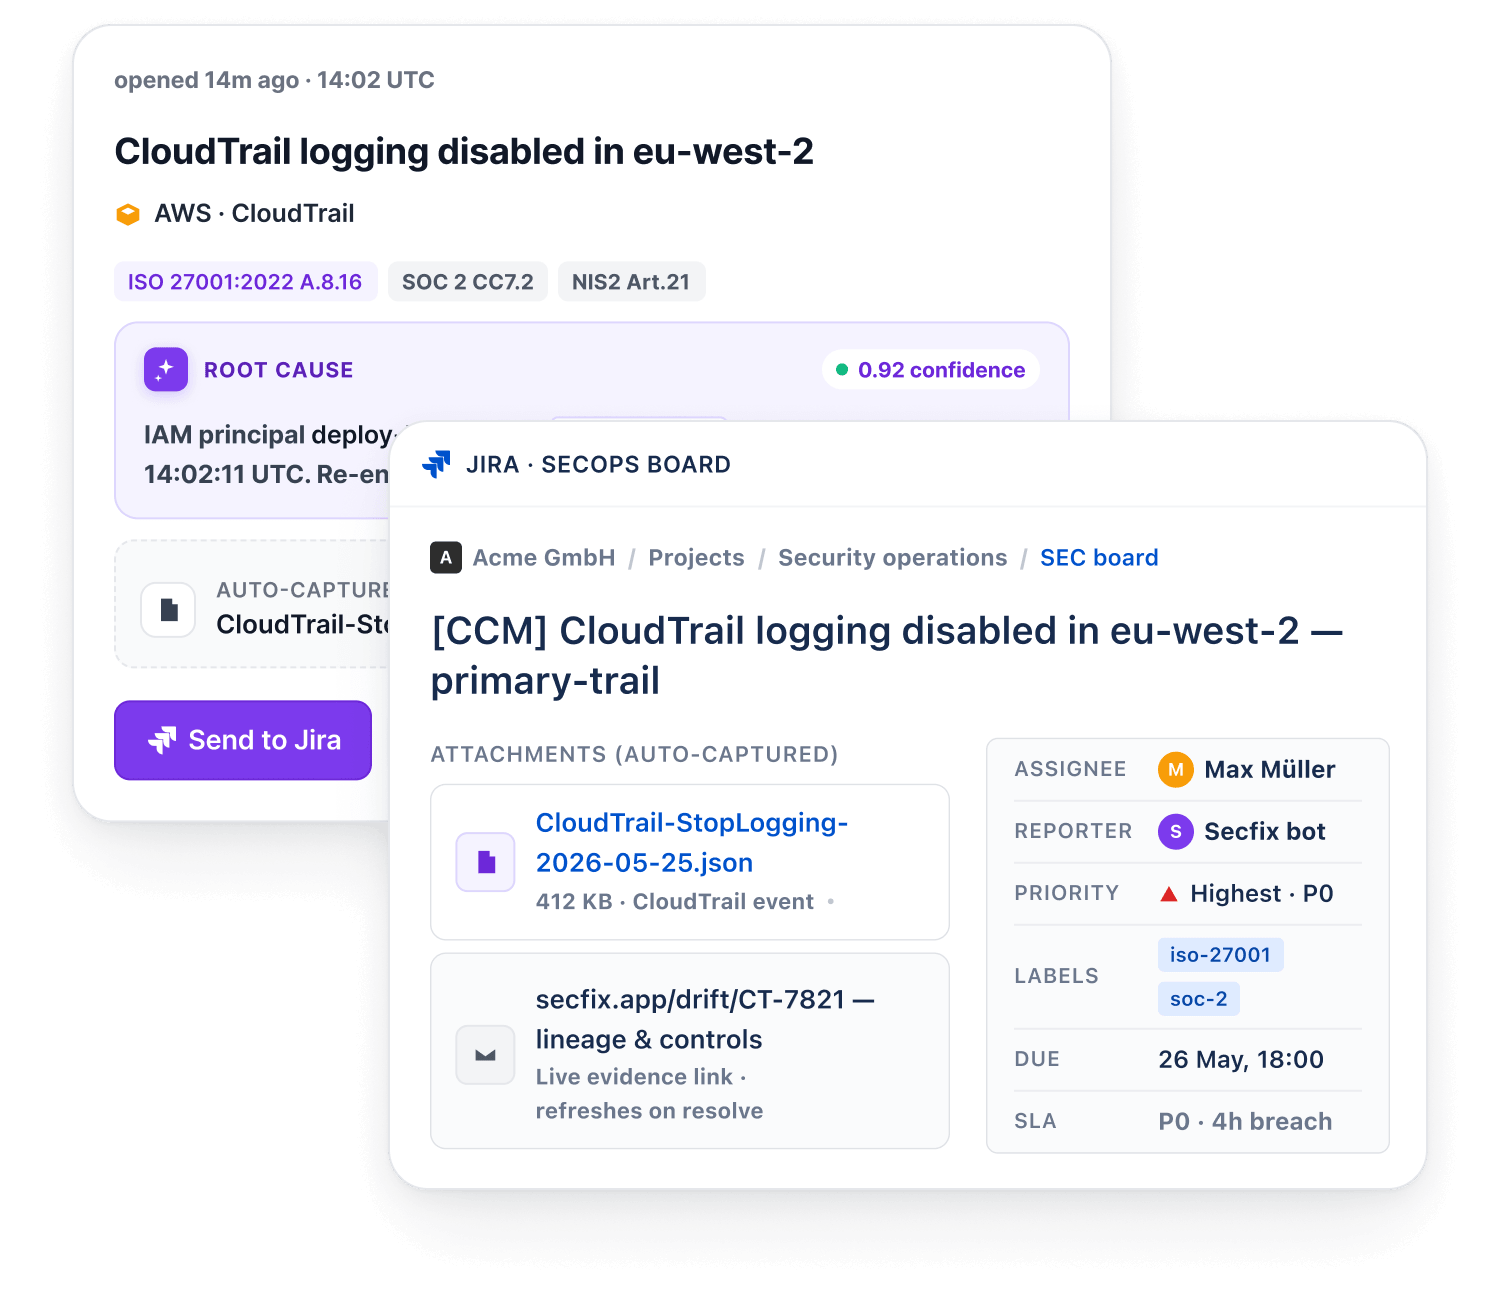
Most teams only know a control is broken when the auditor finds the gap. Secfix runs 250+ checks across your systems, people, devices, and vendors every day, so failures surface the moment they happen.
Owners are assigned automatically and remediation is tracked end to end. Audit week stops being an event.

Mapped to 100+ controls. Ready for every framework.
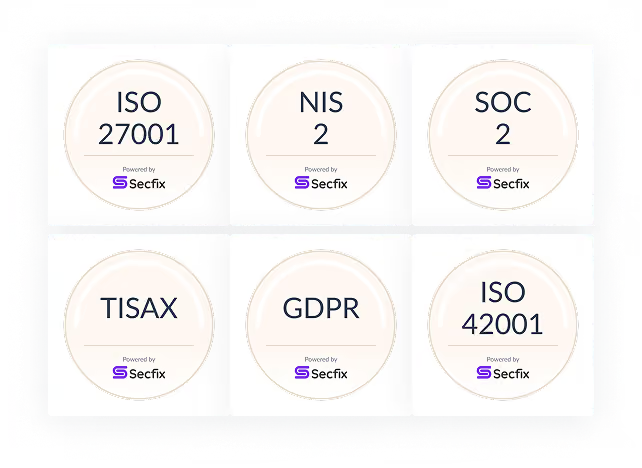
Each check is tied to a specific control across ISO 27001, SOC 2, ISO 42001, NIS2, GDPR, and more. Pass or fail status is logged with a timestamp, an owner, and the underlying evidence. When your auditor asks how a control is enforced, the answer is one click away. The same check covers multiple frameworks, so you don't duplicate work for each certification.
Connected to the systems your business already runs on.
Secfix has 100+ integrations across the tools your team uses every day: Microsoft 365, Google Workspace, Personio, Microsoft Intune, Azure, AWS, GitHub, Jira, Slack, and many more.
Checks run against your actual systems, so evidence stays current automatically. No spreadsheets to update, no screenshots to chase, no compliance reports to assemble by hand.
What our customers say about us

The platform gave us a structure and maturity we couldn’t have achieved on our own. Without it, the process would have taken years, and success in our first audit would have been unlikely.


Secfix combines ease of use with real audit depth. For companies that want to truly live ISO 27001 not just check the box it's the perfect platform.


Secfix enabled us to achieve the ISO 27001 certification swiftly and efficiently, a success we could not have accomplished without them.


For companies that don't have dedicated resources for compliance and certification, trying to manage ISO27001 internally adds unnecessary complexity. With Secfix, we had structure, expertise, and confidence fromday one.


We were impressed by Secfix's all-in-one platform right from the start, and their team's professionalism and expertise made our decision easy. Working with Secfix has strengthened our security system and helped us become a trusted leader in our industry.

Secfix's SaaS platform has been a game-changer for our InfoSec management over the last two years, making everything more organized and boosting our security. The Secfix team always offers help whenever we need. Their tool hasn’t just tidied up our security processes—it’s really taken our security strength to the next level.

Secfix made what seemed like an overwhelming process incredibly smooth and efficient. Their automation and expert support were game-changers for us.


Secfix saved us an enormous amount of time and effort. Everything was pre-filled and well-structured. We no longer had to scramble to find documentation - it was all there, clearly organized.


“Secfix enabled us to achieve the ISO 27001 certification swiftly and efficiently, a success we could not have accomplished without them.”


Secfix has exceeded my expectations in every way. The process of creating security policies was a breeze. Getting ISO 27001 compliant with Secfix is a game-changer for the way that MIXMOVE is able to sell into larger companies. The Customer Success team has proven to be a valuable asset. They are so quick to answer questions, it’s very comforting knowing they’re there for us.

“I’d recommend Secfix in a heartbeat. Secfix made our journey to ISO 27001 certification seamless and fast. "


“The combination of an intuitive platform and knowledgeable team made Secfix the ideal partner for Tanso’s certification journey."


Secfix is more than just software—it’s a partner who could guide you through the entire process. Secfix offered the perfect combination of the right size, good value for money, and the features we actually needed.


“I strongly recommend Secfix to any organization that wants to simplify their compliance management and stick to standards. Secfix’s easy-to-use interface, strong documentation management, and helpful reporting features have been key to our successful ISO certification. For any company looking to improve their compliance efforts and see real results, Secfix is a must-have tool.”


“I recommend Secfix to any company starting the journey of ISO 27001 and TISAX compliance with data protection. Their platform and dedicated support made the process much more manageable. In fact, I have already recommended Secfix to several peers in the industry.”

Secfix is rated a leader on G2
Secfix consistently ranks as a G2 industry leader based on hundreds of customer reviews.
FAQs
What is continuous compliance monitoring?
Continuous compliance monitoring is the practice of automatically checking your security controls every day, instead of only before an audit. Secfix runs 250+ checks across your systems, people, devices, and vendors, and logs every result with a timestamp and owner. Auditors get a clean trail. Your team gets an early warning whenever a control breaks.
How does Secfix automated monitoring work?
Secfix connects to your existing tools through 100+ integrations and pulls evidence directly from your actual systems. Each check is mapped to a specific control across ISO 27001, SOC 2, TISAX, NIS 2, and GDPR. Pass or fail status is logged automatically, and you get an alert the moment a check fails.
Which frameworks does Secfix monitor?
Secfix monitors controls for ISO 27001, SOC 2, TISAX, NIS 2, GDPR, DORA, ISO 9001, ISO 27701, ISO 27018, ISO/IEC 42001, and more. A single check usually covers multiple frameworks, so you don't duplicate work for each certification. New frameworks are added regularly.
Which systems does Secfix integrate with?
Secfix has 100+ integrations across the tools businesses already use: Microsoft 365, Google Workspace, Personio, Microsoft Intune, Azure, AWS, GitHub, Jira, Slack, and many more. Checks run directly against your actual systems, so evidence is always current. No manual export, no screenshot uploads, no spreadsheet updates.
How is continuous monitoring different from a point-in-time audit?
A point-in-time audit shows your controls were working on one specific day. Continuous monitoring shows they are working every day in between. ISO 27001 and SOC 2 both expect ongoing evidence of control effectiveness, not just a one-time snapshot, and continuous monitoring is how teams meet that requirement without manual checks.
What happens when a Secfix check fails?
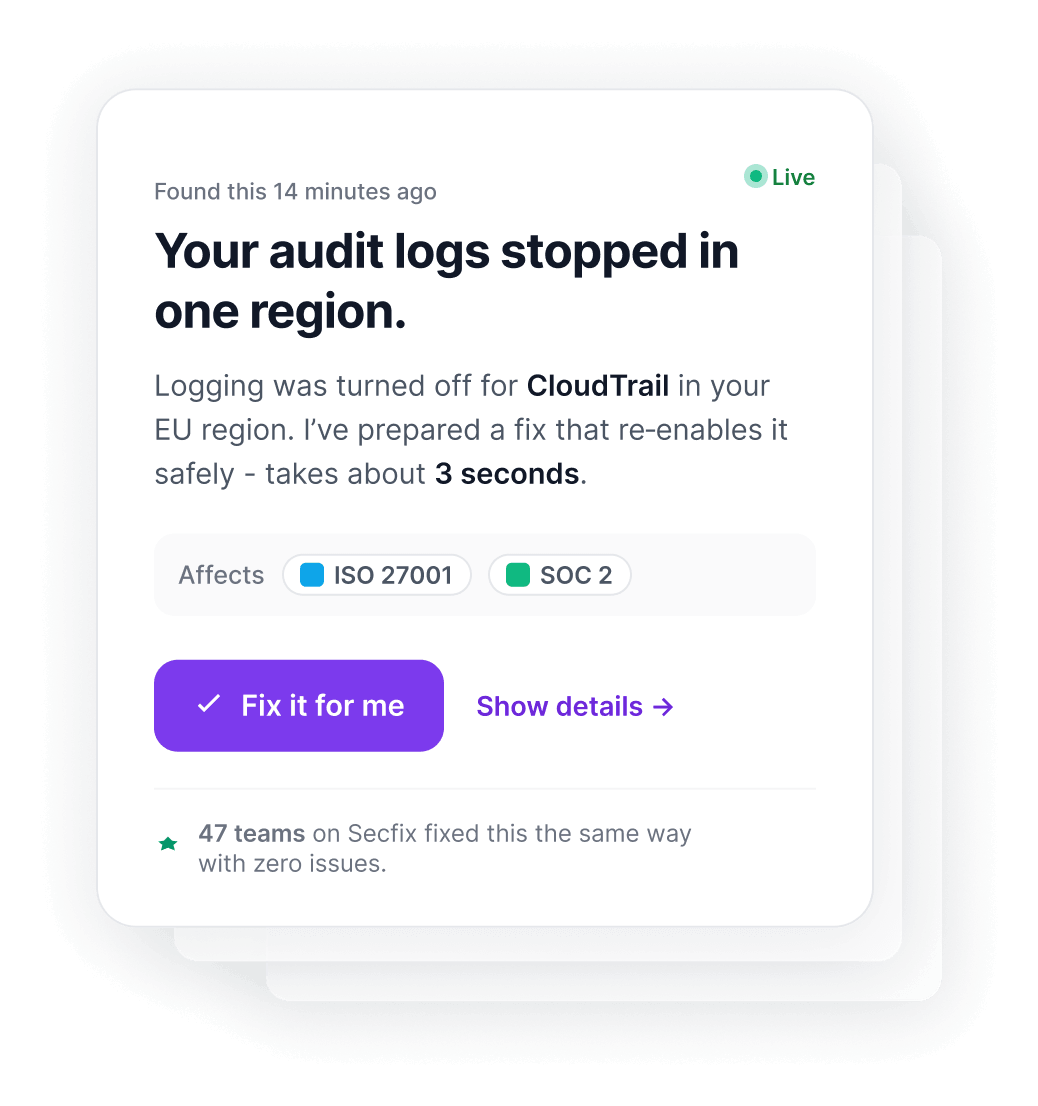
A failed check creates an alert, assigns the right owner, and gives clear remediation steps. The issue is tracked until it's resolved, and a full audit trail is kept for your next audit. You see the same status your auditor will see, with no preparation required.
Does my auditor accept evidence from Secfix?
Yes. Secfix is built in Germany and designed for European auditors from day one. The evidence trail meets the requirements of ISO 27001, SOC 2, TISAX, and other major frameworks, and Secfix has supported 1000+ audits across DACH and the rest of Europe.
Do I need an internal CISO to run continuous monitoring?
No. Secfix is built for SMB and mid-market teams that often don't have a dedicated CISO. The platform runs the checks, assigns owners, and flags what needs attention. For teams that want full coverage, Secfix offers CISOaaS, a dedicated security and compliance expert who owns your monitoring program end-to-end.