
All the policies you need for your ISMS without manual effort
Generate your policies with Secfix or upload your own and map them to your controls, then handle approvals, employee sign-off, and version history in one place.
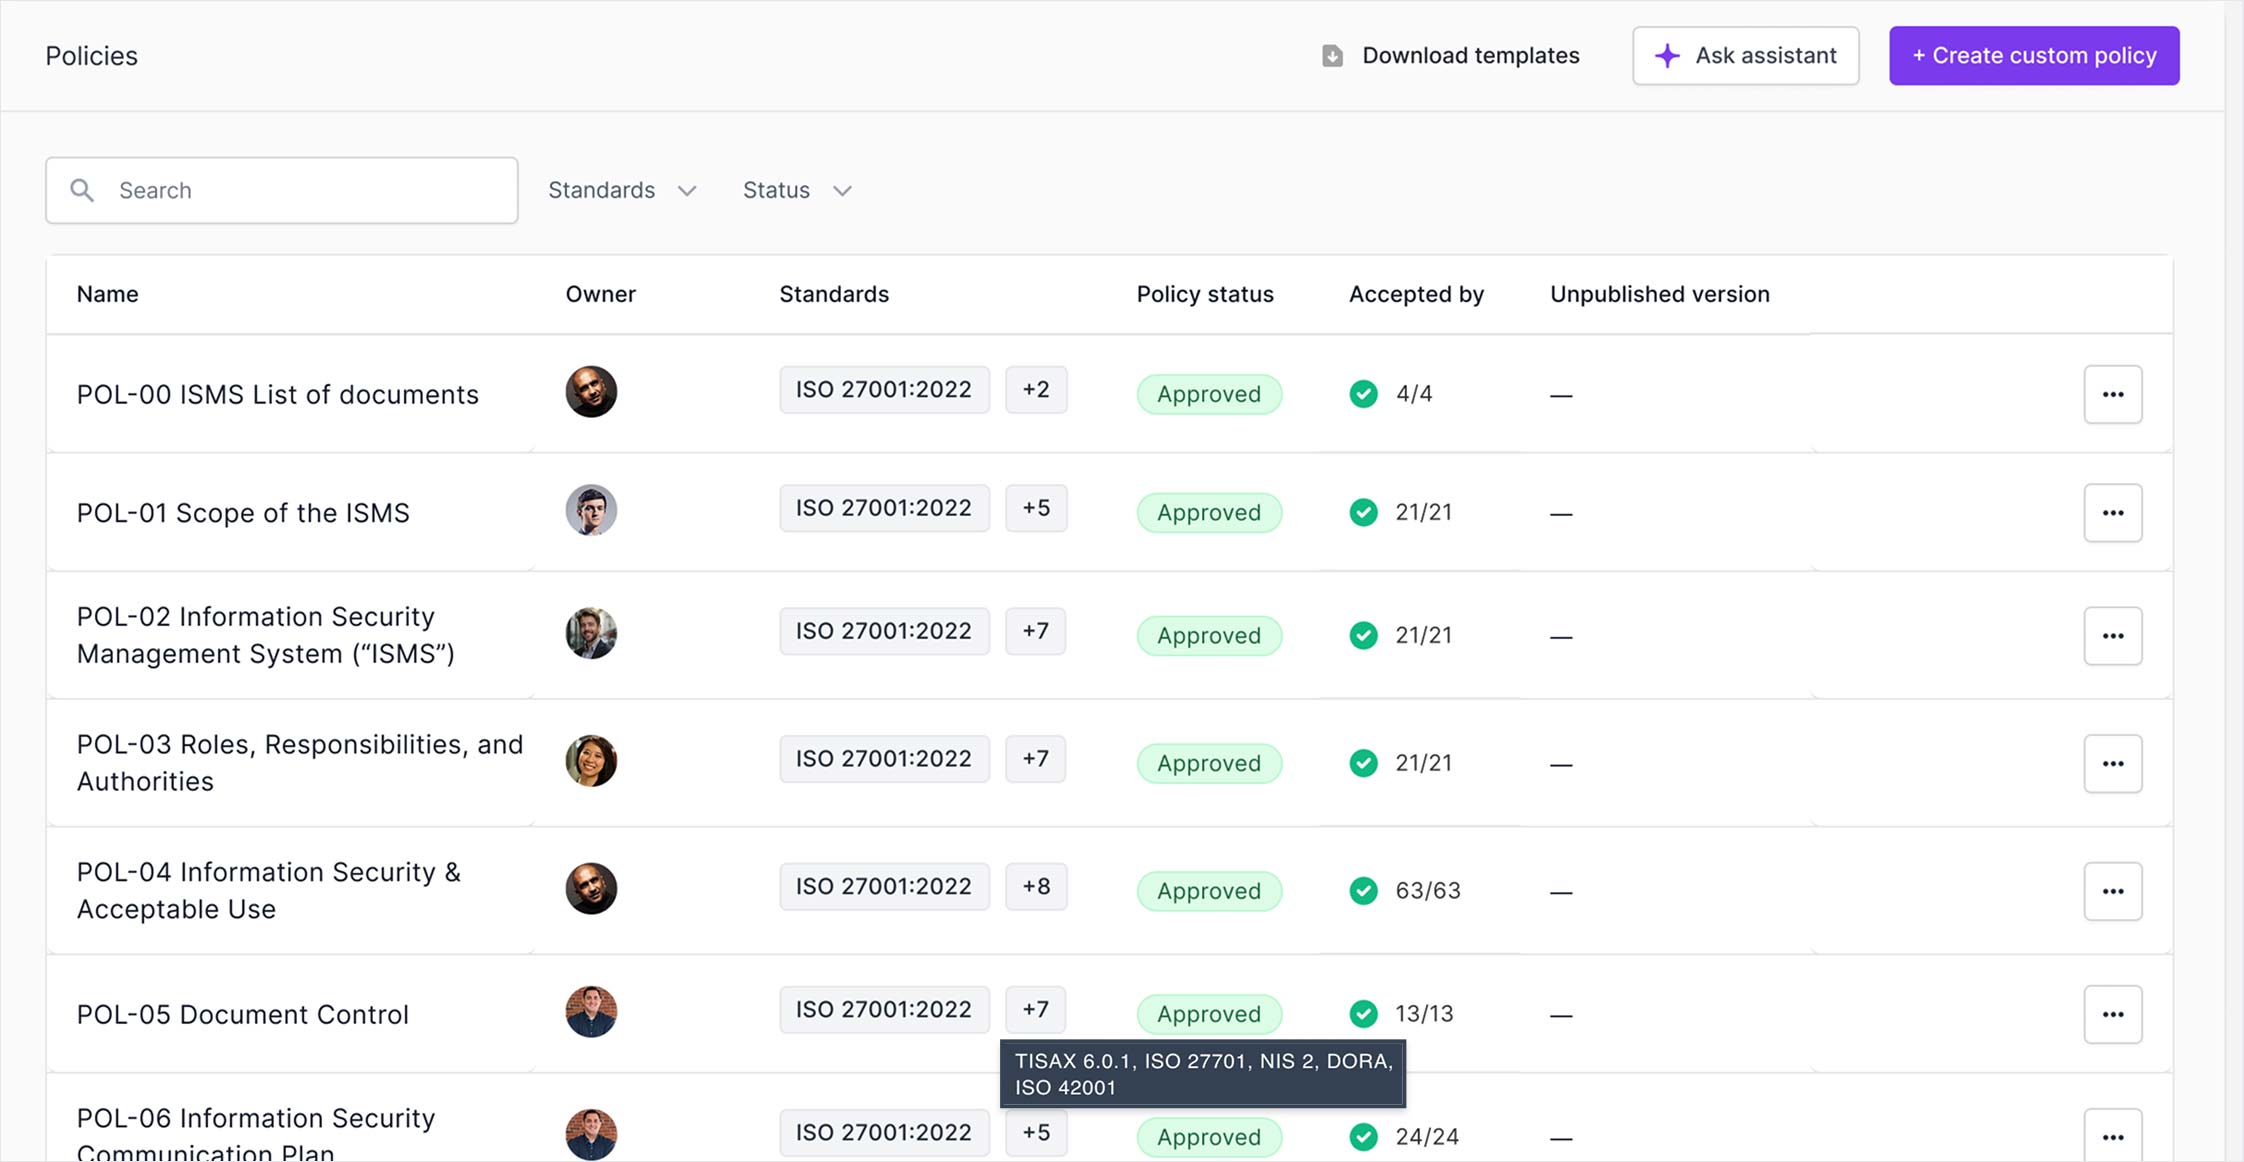


Generate your policies or bring your own
You do not have to build policies from scratch. Use the Secfix policy generator to create them from your business and scope, or upload the policies you already have and map them to your controls.
Either way, Secfix recommends what to improve based on what works across 1000+ audits, so gaps show up before your auditor finds them. You reach a complete, defensible set of policies without a security hire.

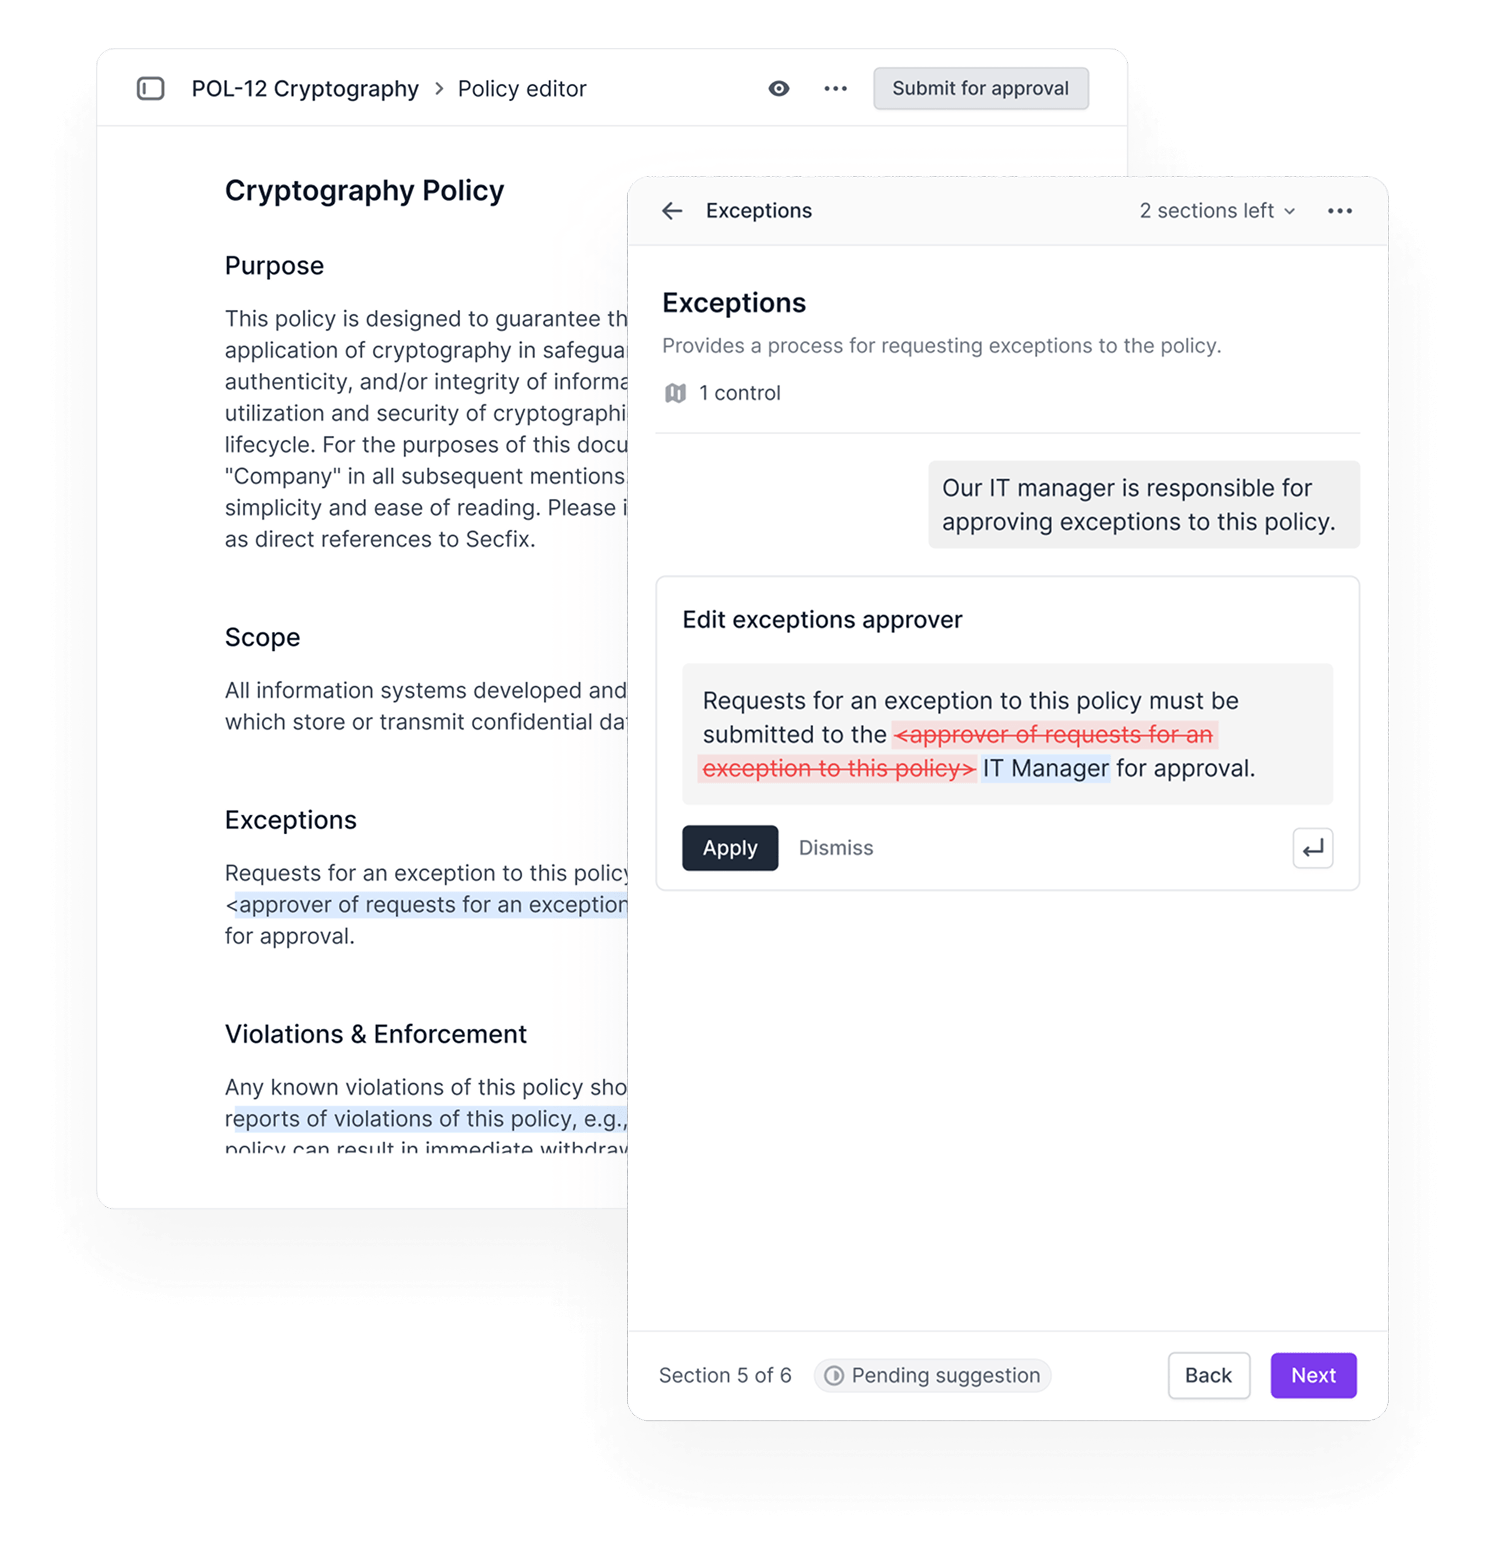
Automate approvals and employee sign-off
A policy only counts once it is approved and read by the right people. Secfix takes each policy through review and approval, then collects employee sign-off in the same place, so you do not chase signatures through a separate tool.
Assign policies to the groups they apply to, so employees only read what fits their role, and see who has signed at a glance. When your auditor asks who approved a policy and who accepted it, the record is already there.
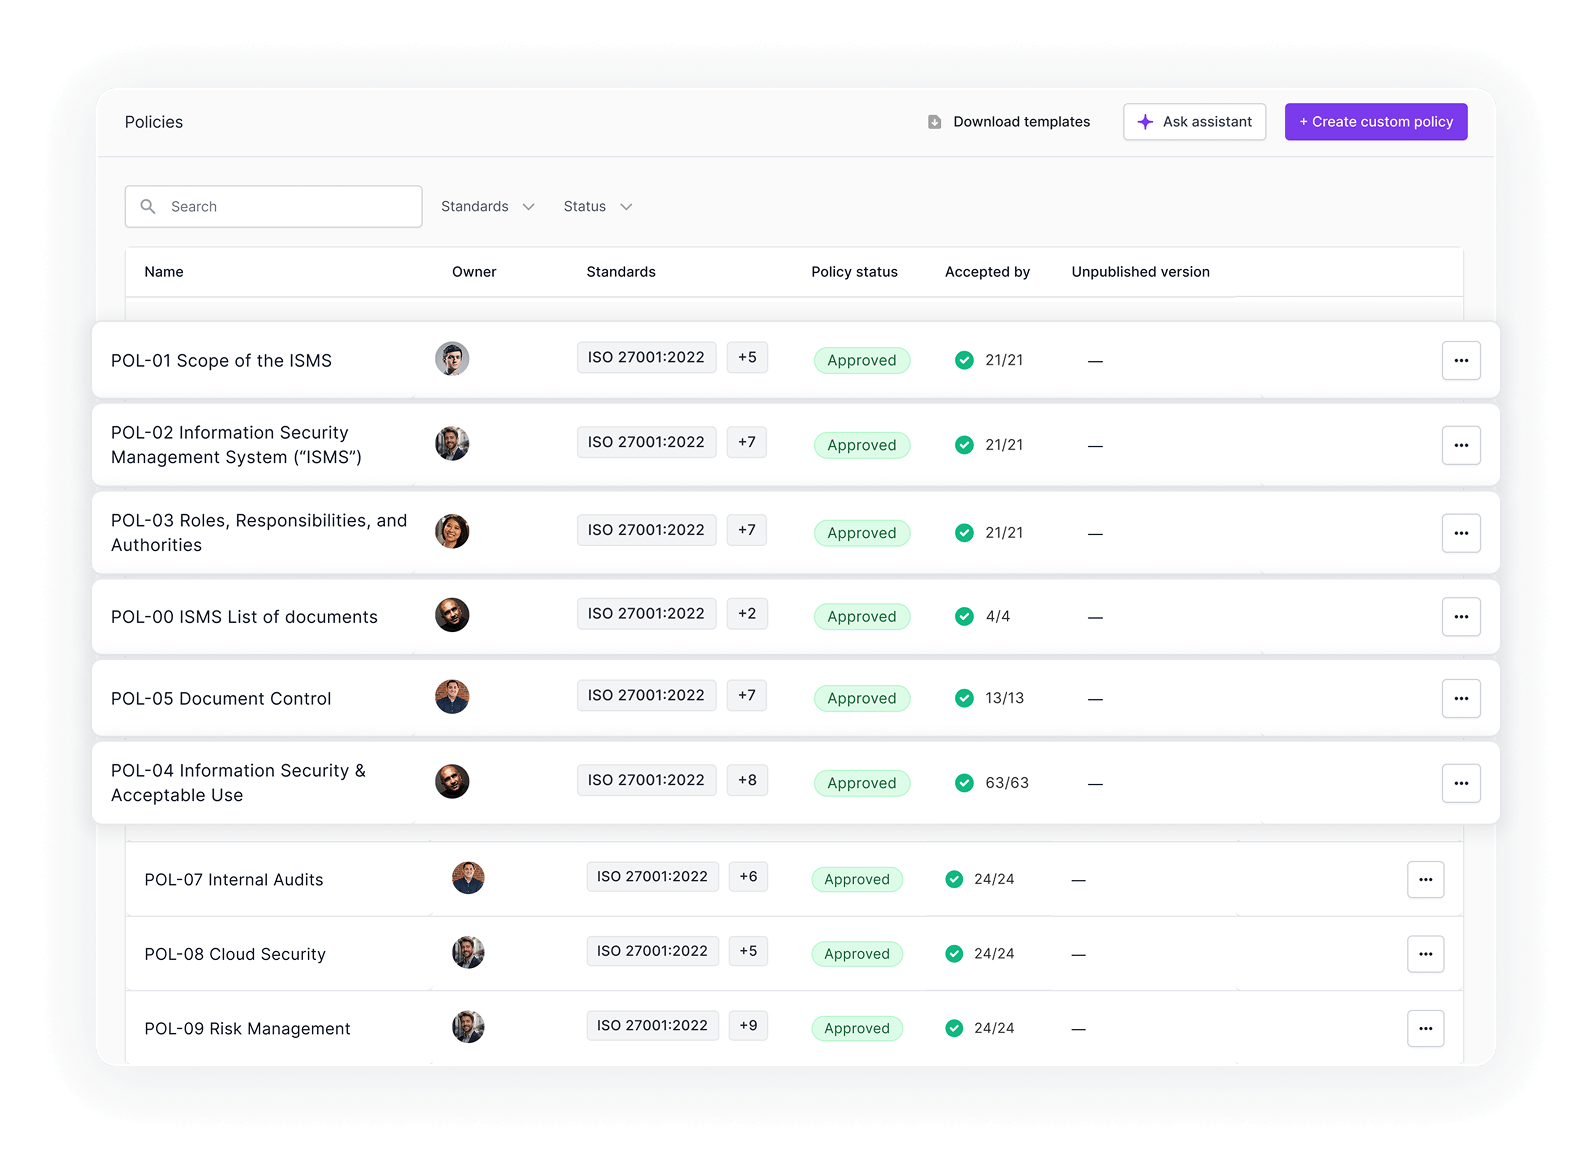
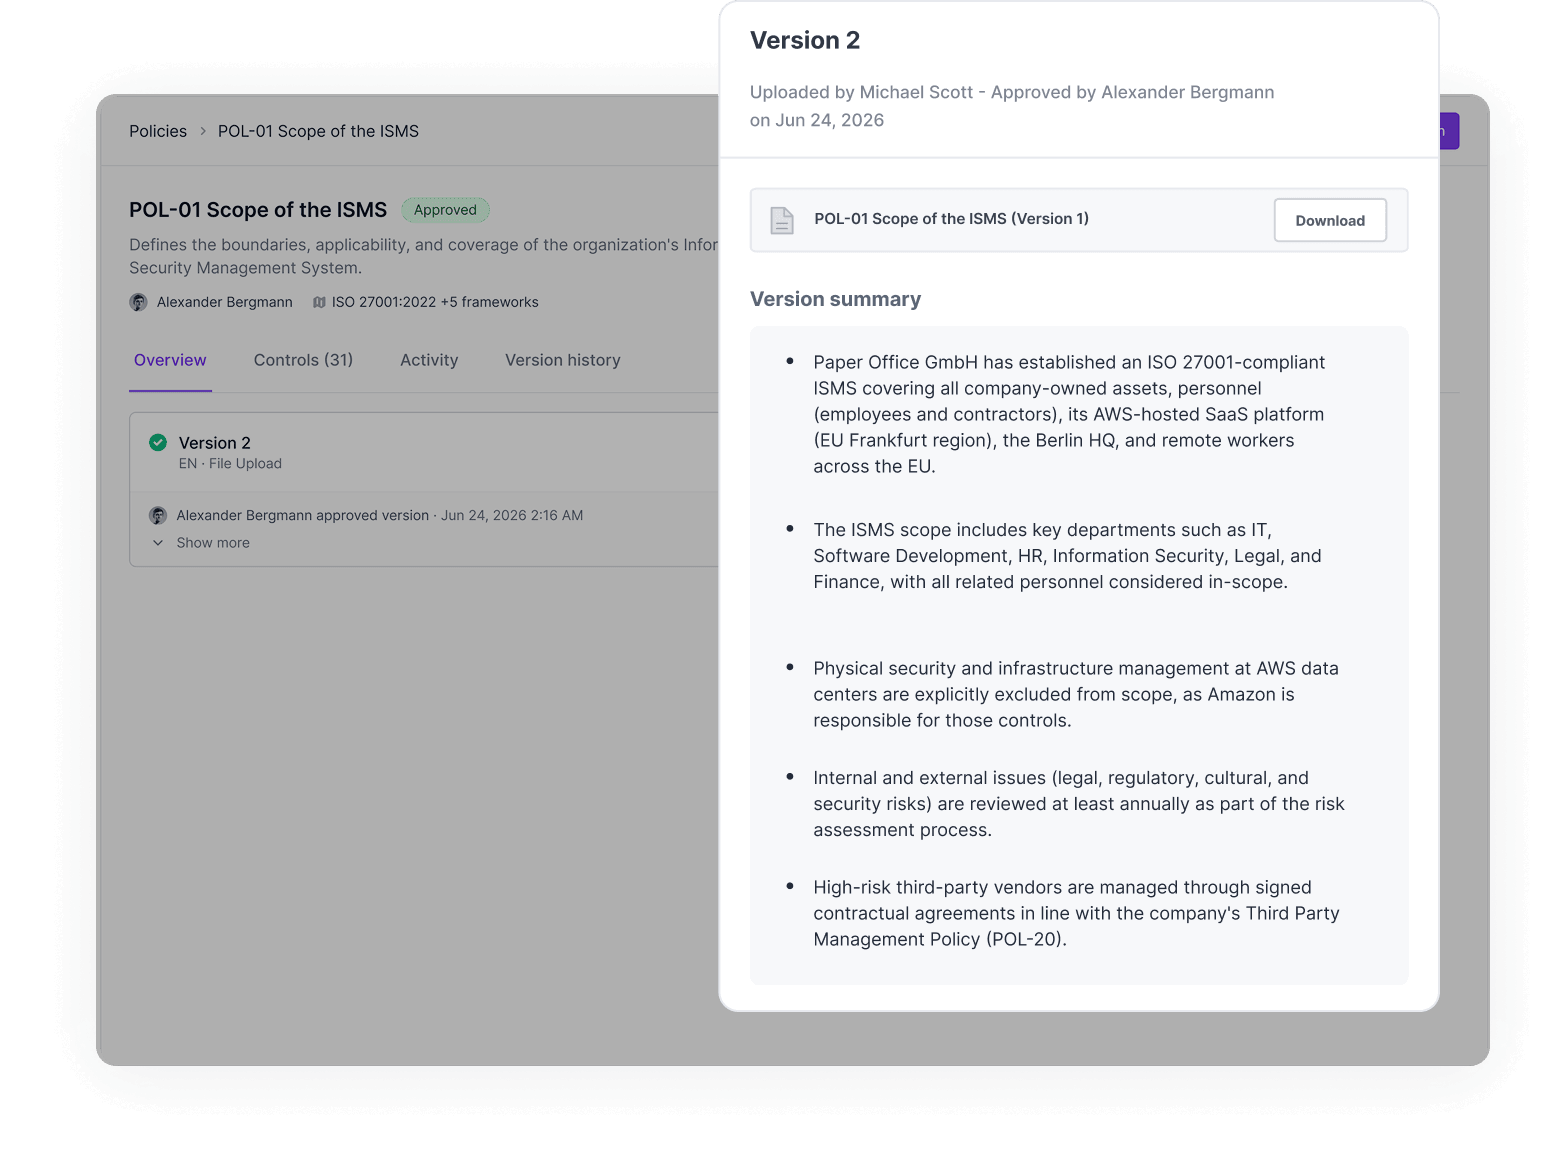
Every version and change, tracked in one place
Policies change, and auditors want to see how. CISO AI keeps a full version history for every policy, with a plain summary of what changed between versions, so you track your policies in one place instead of across email and shared drives.
Reminders arrive before each annual review, so nothing lapses between certifications. Your policies stay current, and the history behind them is always ready for audit.
What our customers say about us

“Secfix enabled us to achieve the ISO 27001 certification swiftly and efficiently, a success we could not have accomplished without them.”


“I’d recommend Secfix in a heartbeat. Secfix made our journey to ISO 27001 certification seamless and fast. "


“The combination of an intuitive platform and knowledgeable team made Secfix the ideal partner for Tanso’s certification journey."


“Secfix is more than just software—it’s a partner who could guide you through the entire process. Secfix offered the perfect combination of the right size, good value for money, and the features we actually needed. "


“I strongly recommend Secfix to any organization that wants to simplify their compliance management and stick to standards. Secfix’s easy-to-use interface, strong documentation management, and helpful reporting features have been key to our successful ISO certification. For any company looking to improve their compliance efforts and see real results, Secfix is a must-have tool.”


“I recommend Secfix to any company starting the journey of ISO 27001 and TISAX compliance with data protection. Their platform and dedicated support made the process much more manageable. In fact, I have already recommended Secfix to several peers in the industry.”

Secfix is rated a leader on G2
Secfix consistently ranks as a G2 industry leader based on hundreds of customer reviews.
FAQs
What are information security policies?
Information security policies are the written rules that define how an organisation protects information: responsibilities, acceptable use, access, supplier handling, and incident response. They form the core of an Information Security Management System (ISMS) and are the documents auditors review first. Standards including ISO 27001, SOC 2, TISAX, NIS 2, ISO 42001 all require these policies to be approved by management and shared with the people they apply to.
Which frameworks does Secfix policy management support?
Secfix supports policy management for ISO 27001, SOC 2, TISAX, GDPR, DORA, ISO 42001, NIS2 and more. You keep one policy base and map it to the controls for each standard, so a policy you write or upload once can satisfy several frameworks at the same time. Most customers start with ISO 27001 and add further standards later without rebuilding their policies.
Which policies do you need for ISO 27001?
ISO 27001 requires a top-level information security policy plus supporting policies covering the Annex A controls relevant to your scope, such as access control, supplier management, human resources security, and acceptable use. Many of these same policies also serve SOC 2, NIS2, TISAX. Secfix maps your policies to 100+ pre-built controls, so you cover what each standard needs without guessing.
Do you have to write your policies from scratch?
No. Secfix gives you two ways to avoid a blank page: generate your policies from your business and scope, or upload the policies you already have and map them to your controls. Either way, Secfix recommends improvements based on what works across 1000+ audits, and you review and approve the result rather than writing everything yourself. The same applies across ISO 27001, SOC 2, TISAX, ISO 42001 and the other standards Secfix supports.
Who needs to approve security policies?
Security policies must be formally approved by management before they take effect, and re-approved whenever they change. This holds across ISO 27001, SOC 2, TISAX, and similar standards. In practice the approver is usually the person accountable for security, such as a CISO, Head of IT, or Geschäftsführer. Secfix records each approval with a full version history, so the approval trail is ready when your auditor asks.
How does Secfix keep policies audit-ready?
Secfix keeps every policy in one place with a full version history, a plain summary of what changed between versions, recorded approvals, and tracked employee sign-off. Reminders arrive before each review, so nothing lapses. When your auditor asks for a policy, its history, or who approved and accepted it, the record is already complete, whether the audit is for ISO 27001, SOC 2, TISAX, or another standard.
Get your policies audit-ready
Generate your policies or upload your own, then approve, sign off, and track them in one place.