
Manage every risk in one platform
Secfix replaces your risk spreadsheets with an automated risk register pre-mapped to 100+ controls across ISO 27001, SOC 2, NIS 2, and more
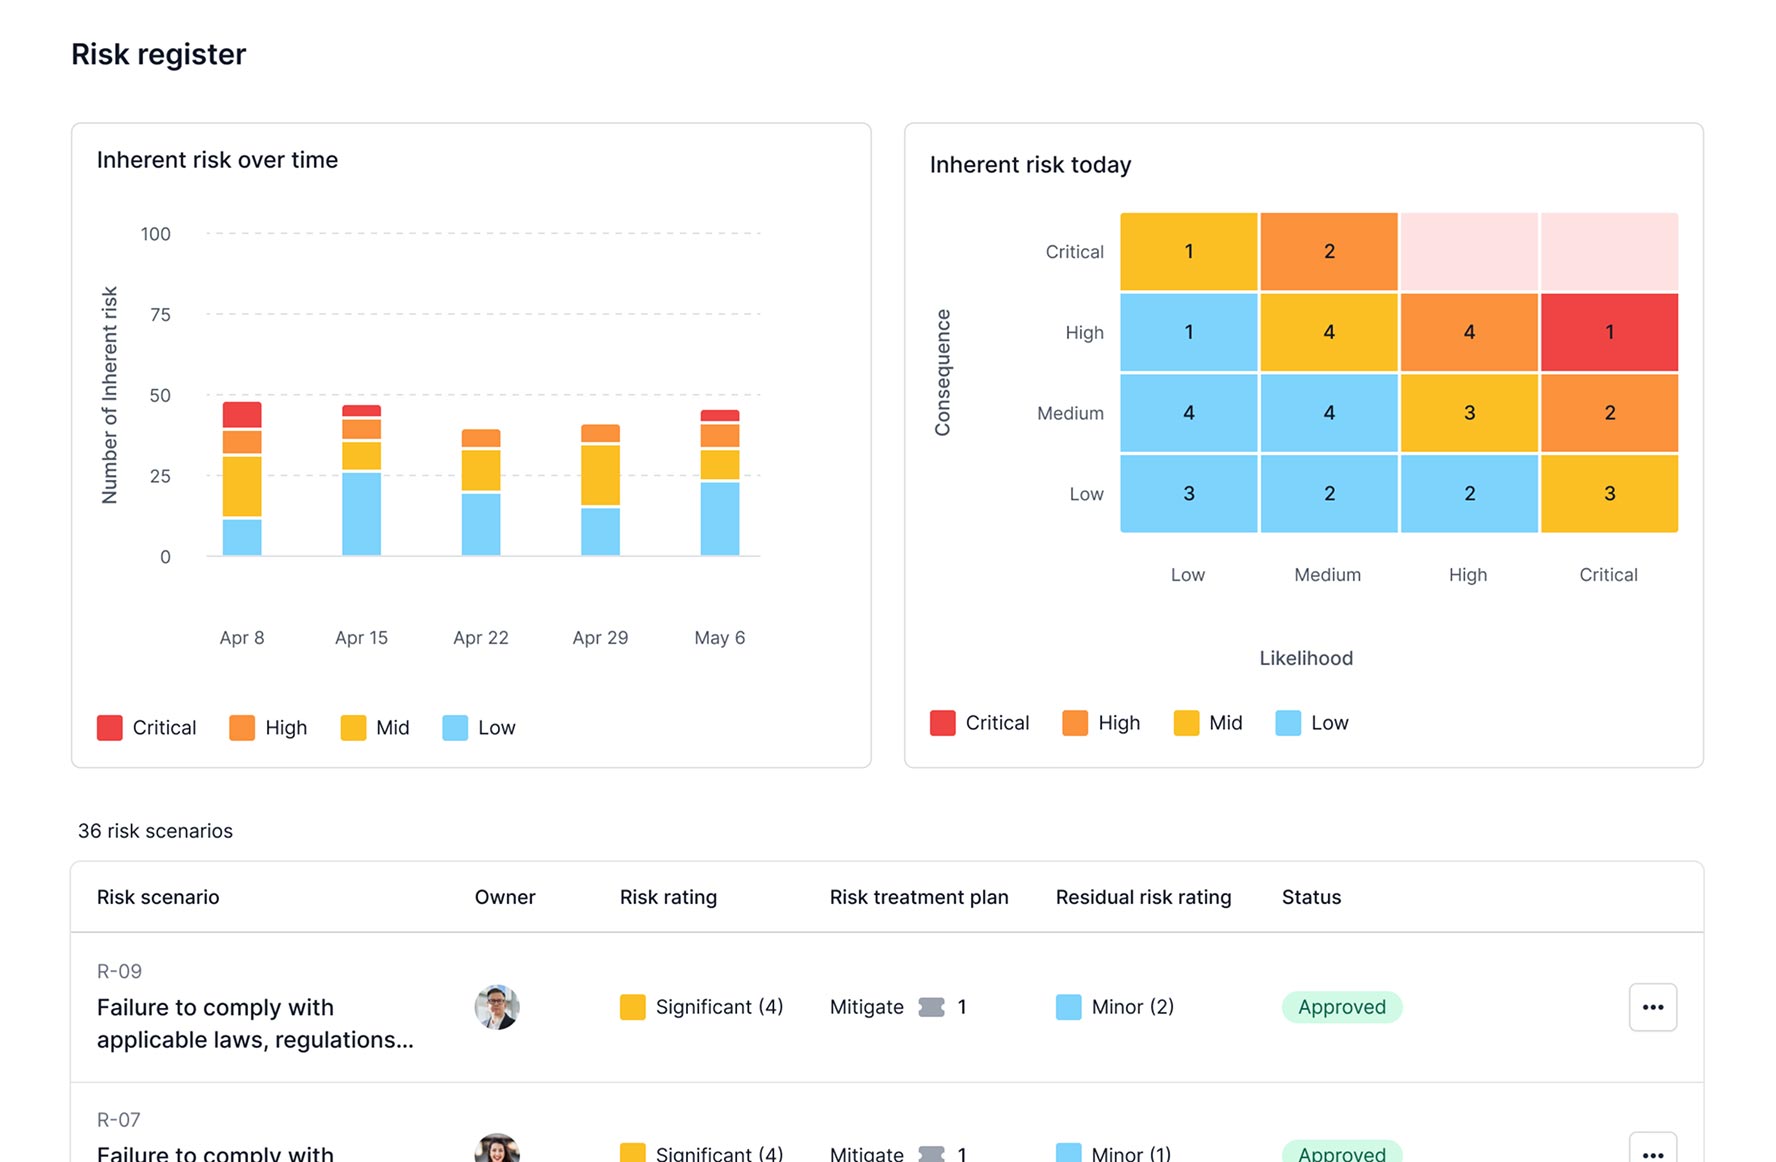



Off the risk register spreadsheet. Into one workflow.
Most risk registers live on a shared drive, lose their owners between reviews, and quietly stop matching the controls they're supposed to treat. Secfix replaces all of it with pre-built risk scenarios, automatic owner assignment, scheduled quarterly reviews, and a full audit trail of every change.
Your team stops maintaining the register. They start working through it.

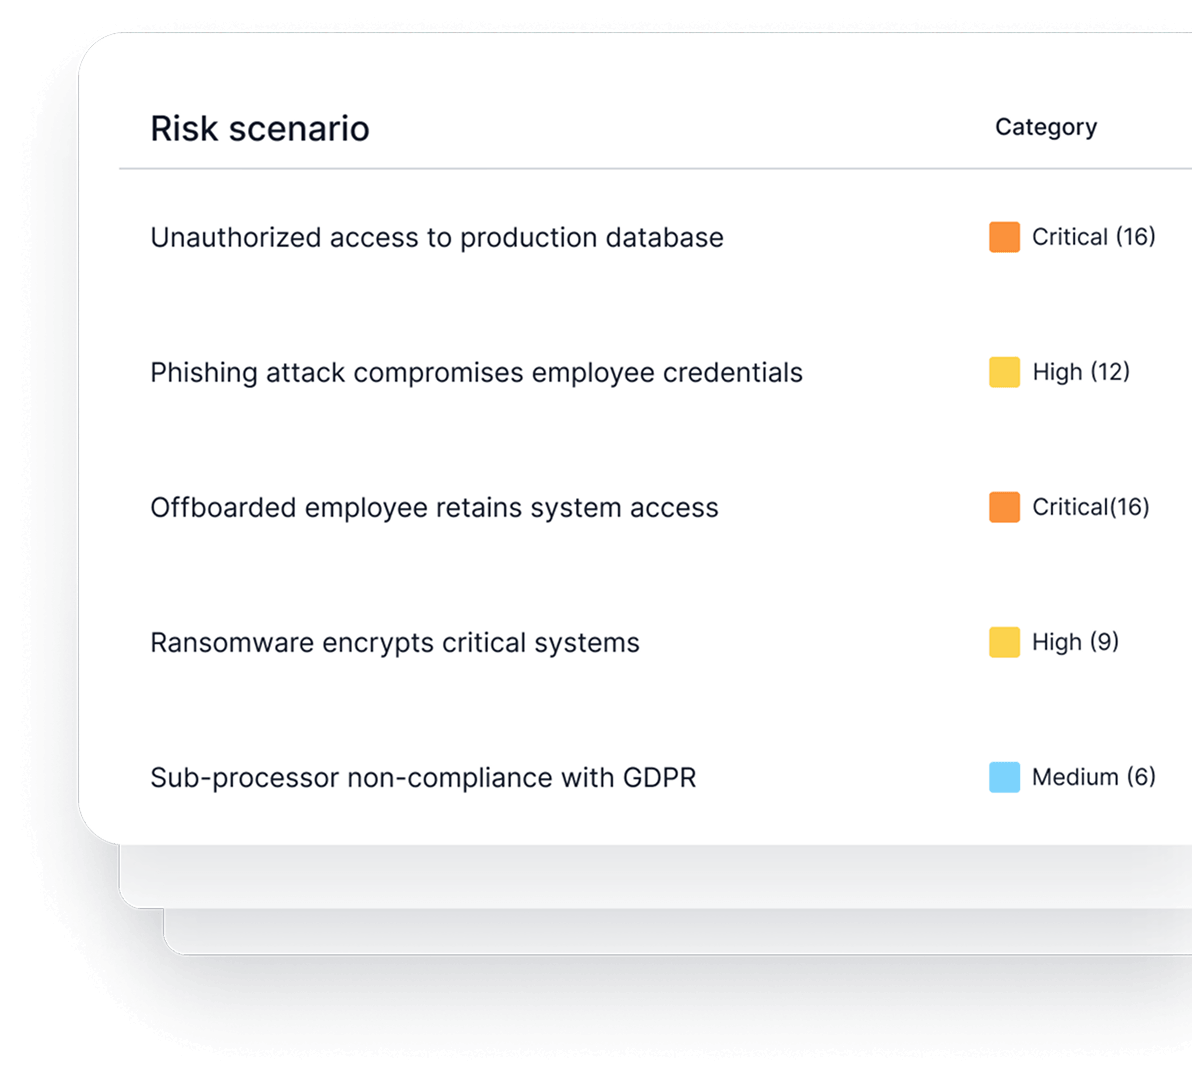
Built on ISO 27005. One risk register, every framework.
Secfix follows the full ISO 27005 lifecycle: identification, analysis, evaluation, treatment, and monitoring. The same risk scenario can be mapped to ISO 27001, SOC 2, TISAX, GDPR controls and more automatically, so you stop maintaining a separate register for each framework. Assess once, certify against many.
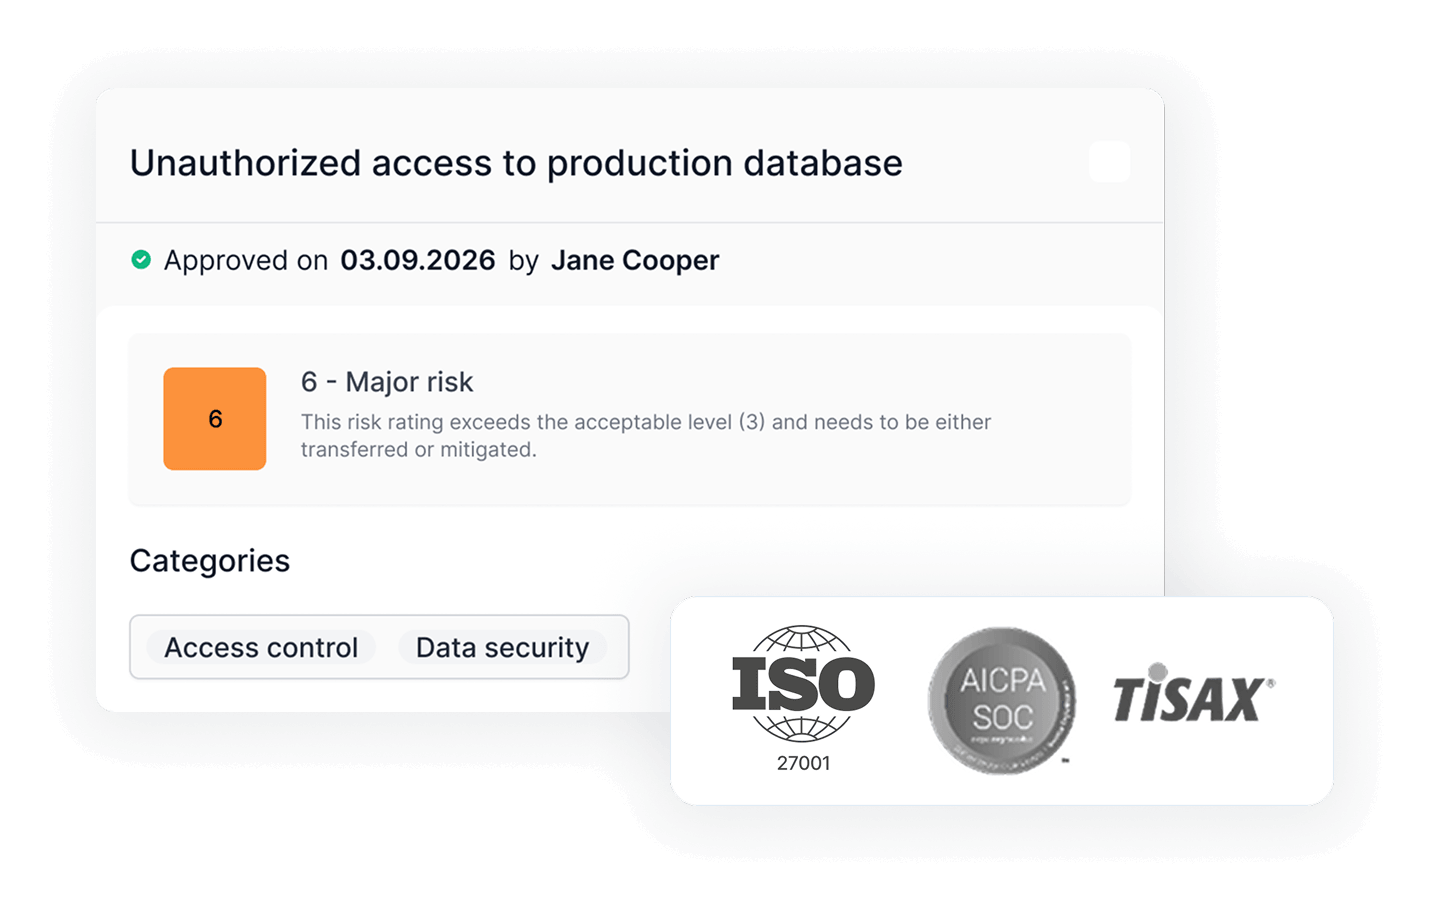
Every risk, connected to the rest of your ISMS
Risks don't live in isolation. Every risk scenario is linked to controls, evidence, policies that document them, and the vendors that introduce them. Your risk register stops being a separate document. It becomes the operational map your company uses to run security and your auditor uses to verify it.

What our customers say about us

The platform gave us a structure and maturity we couldn’t have achieved on our own. Without it, the process would have taken years, and success in our first audit would have been unlikely.


Secfix combines ease of use with real audit depth. For companies that want to truly live ISO 27001 not just check the box it's the perfect platform.


Secfix enabled us to achieve the ISO 27001 certification swiftly and efficiently, a success we could not have accomplished without them.


For companies that don't have dedicated resources for compliance and certification, trying to manage ISO27001 internally adds unnecessary complexity. With Secfix, we had structure, expertise, and confidence fromday one.


We were impressed by Secfix's all-in-one platform right from the start, and their team's professionalism and expertise made our decision easy. Working with Secfix has strengthened our security system and helped us become a trusted leader in our industry.

Secfix's SaaS platform has been a game-changer for our InfoSec management over the last two years, making everything more organized and boosting our security. The Secfix team always offers help whenever we need. Their tool hasn’t just tidied up our security processes—it’s really taken our security strength to the next level.

Secfix made what seemed like an overwhelming process incredibly smooth and efficient. Their automation and expert support were game-changers for us.


Secfix saved us an enormous amount of time and effort. Everything was pre-filled and well-structured. We no longer had to scramble to find documentation - it was all there, clearly organized.


“Secfix enabled us to achieve the ISO 27001 certification swiftly and efficiently, a success we could not have accomplished without them.”


Secfix has exceeded my expectations in every way. The process of creating security policies was a breeze. Getting ISO 27001 compliant with Secfix is a game-changer for the way that MIXMOVE is able to sell into larger companies. The Customer Success team has proven to be a valuable asset. They are so quick to answer questions, it’s very comforting knowing they’re there for us.

“I’d recommend Secfix in a heartbeat. Secfix made our journey to ISO 27001 certification seamless and fast. "


“The combination of an intuitive platform and knowledgeable team made Secfix the ideal partner for Tanso’s certification journey."


Secfix is more than just software—it’s a partner who could guide you through the entire process. Secfix offered the perfect combination of the right size, good value for money, and the features we actually needed.


“I strongly recommend Secfix to any organization that wants to simplify their compliance management and stick to standards. Secfix’s easy-to-use interface, strong documentation management, and helpful reporting features have been key to our successful ISO certification. For any company looking to improve their compliance efforts and see real results, Secfix is a must-have tool.”


“I recommend Secfix to any company starting the journey of ISO 27001 and TISAX compliance with data protection. Their platform and dedicated support made the process much more manageable. In fact, I have already recommended Secfix to several peers in the industry.”

Secfix is rated a leader on G2
Secfix consistently ranks as a G2 industry leader based on hundreds of customer reviews.
FAQs
What is a risk register?
A risk register is a documented list of the information security risks your organisation faces, scored by likelihood and impact, with assigned owners and treatment plans. ISO 27001 requires one and expects evidence that it's reviewed and updated continuously. Secfix replaces the spreadsheet version with a live register pre-populated with 100+ risks mapped to your frameworks.
How does Secfix score risks?
Secfix scores each risk against confidentiality, integrity, and availability using a methodology aligned with ISO 27005. You can adjust likelihood and impact thresholds for your organisation, and every score is linked to the controls and policies that treat the risk. Auditors see the full trace from identification to treatment in one view.
Can I import my existing risk catalog?
Yes. Secfix supports bulk import of risk catalogs from Excel. Treatment plans, owners, and deadlines can be assigned in the platform after import, and every imported risk can be mapped to the relevant controls of ISO 27001, SOC 2, TISAX, ISO 42001, GDPR, and more.
How does the risk register stay up to date?
The register updates continuously as new risks emerge from the risk assessments you conduct in Secfix. Outdated risks are archived with a full audit trail, so your auditor sees real activity across the year, not a spreadsheet refreshed the week before.
Can I manage risk in Secfix without a CISO?
Yes. Secfix is built for SMB and mid-market teams that don't always have a dedicated CISO in seat. The platform handles methodology, scoring, and control mapping, and every customer gets a dedicated Customer Success Manager. Teams that want a CISO without hiring one can add CISOaaS on top of the platform.
Does the risk register cover multiple frameworks at once?
Yes. One risk register feeds ISO 27001, SOC 2, TISAX, GDPR, NIS 2, DORA and more frameworks. Each risk maps to the relevant controls across every framework you're certified against, so adding a second framework doesn't mean rebuilding the register.