
Security compliance for mid-market companies
All your frameworks, all your entities, and every team in one platform. A system for your compliance that lasts, without the complexity.



Run every framework from one control set
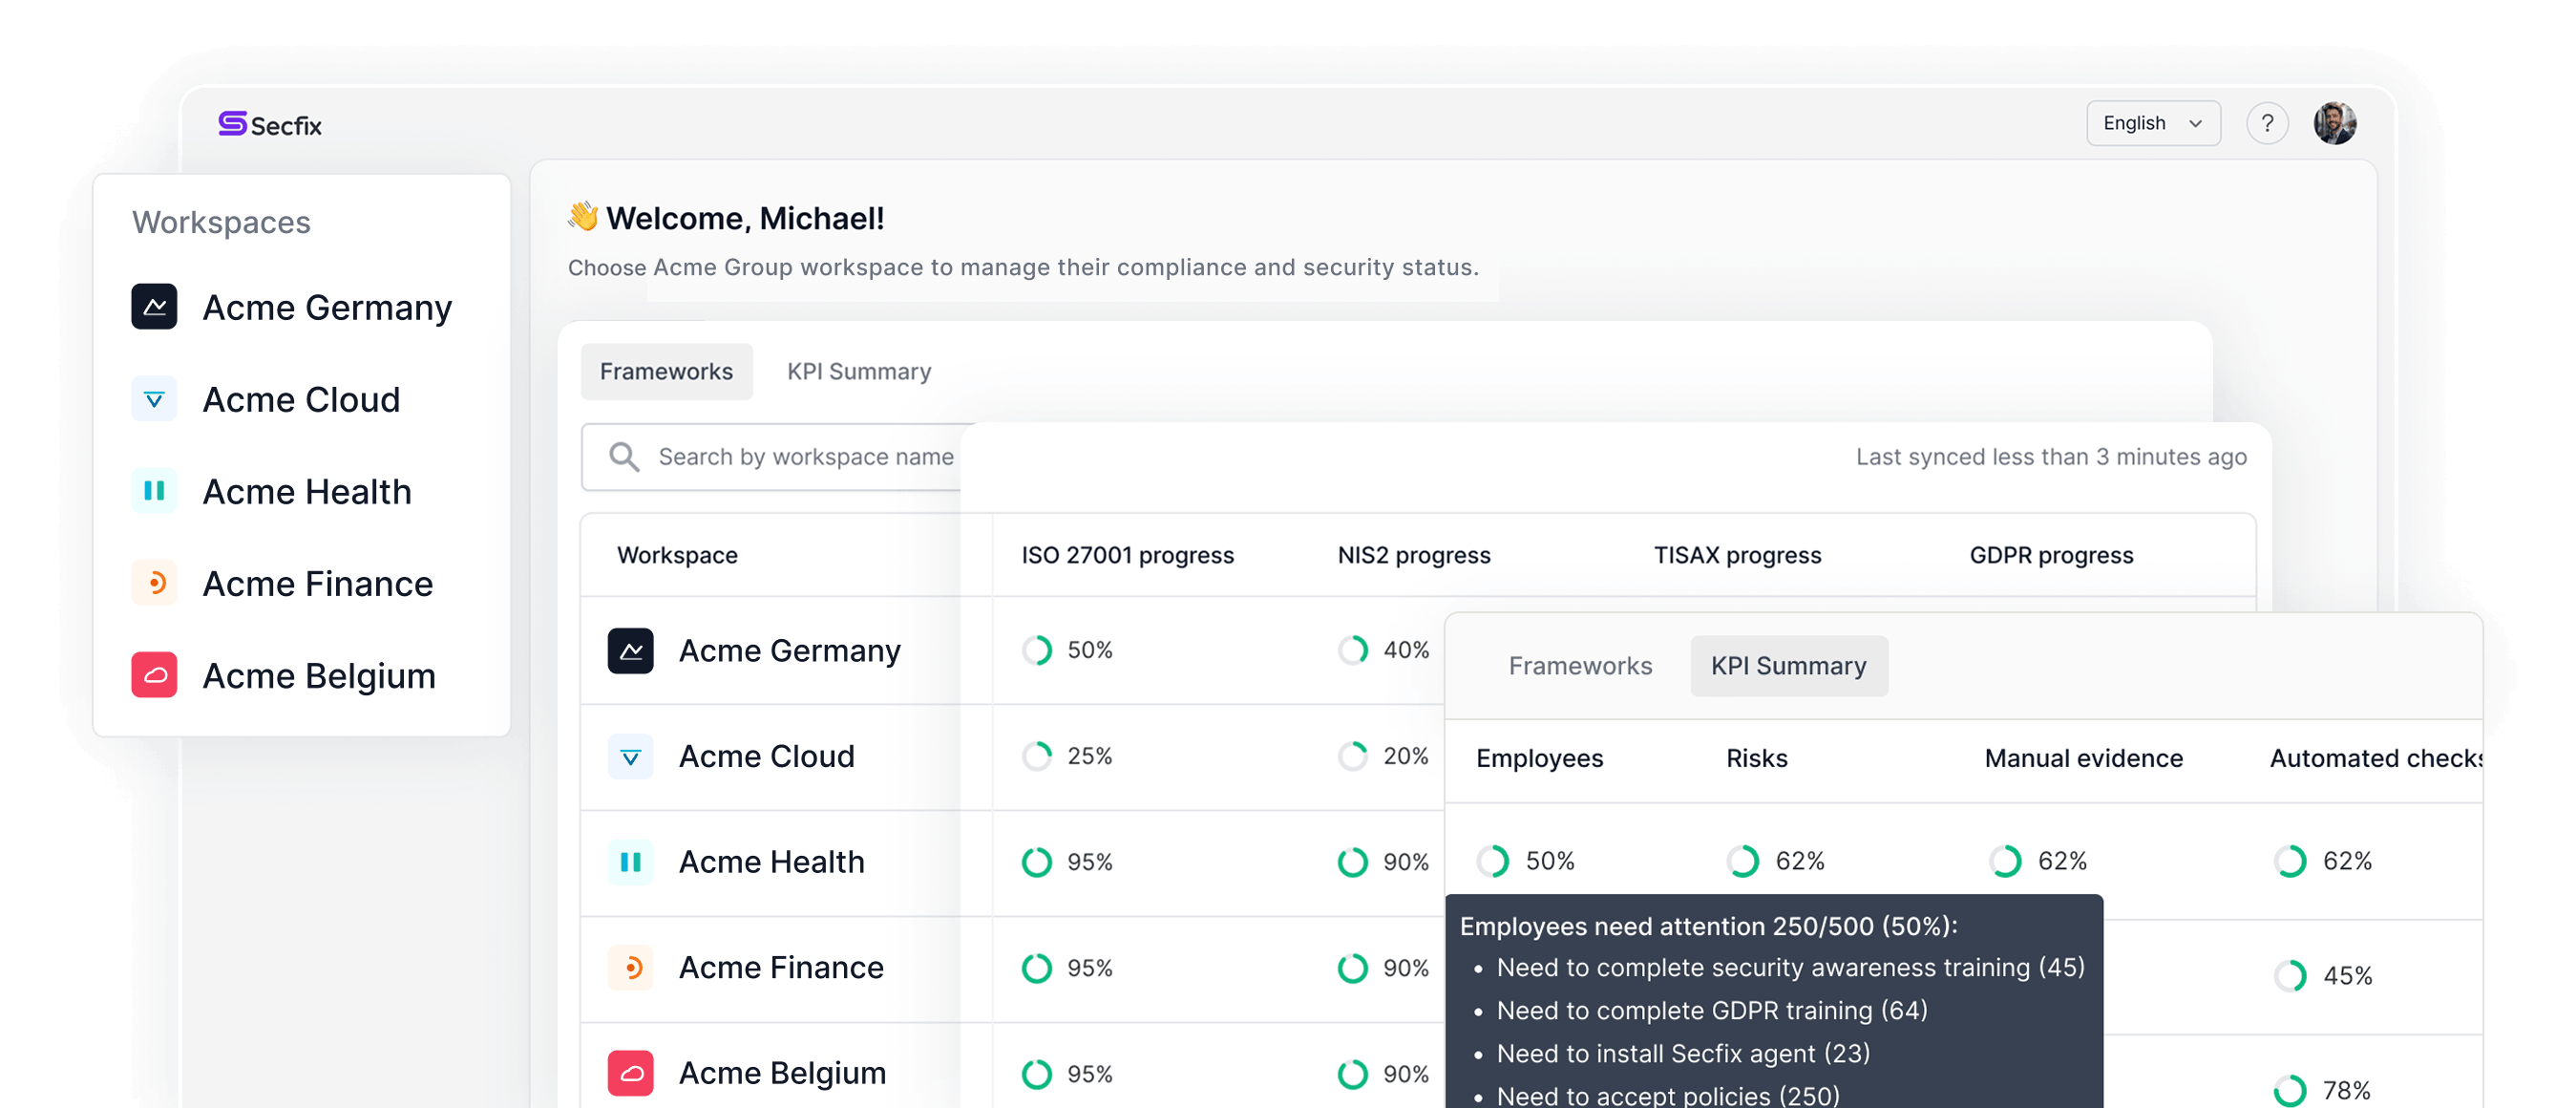
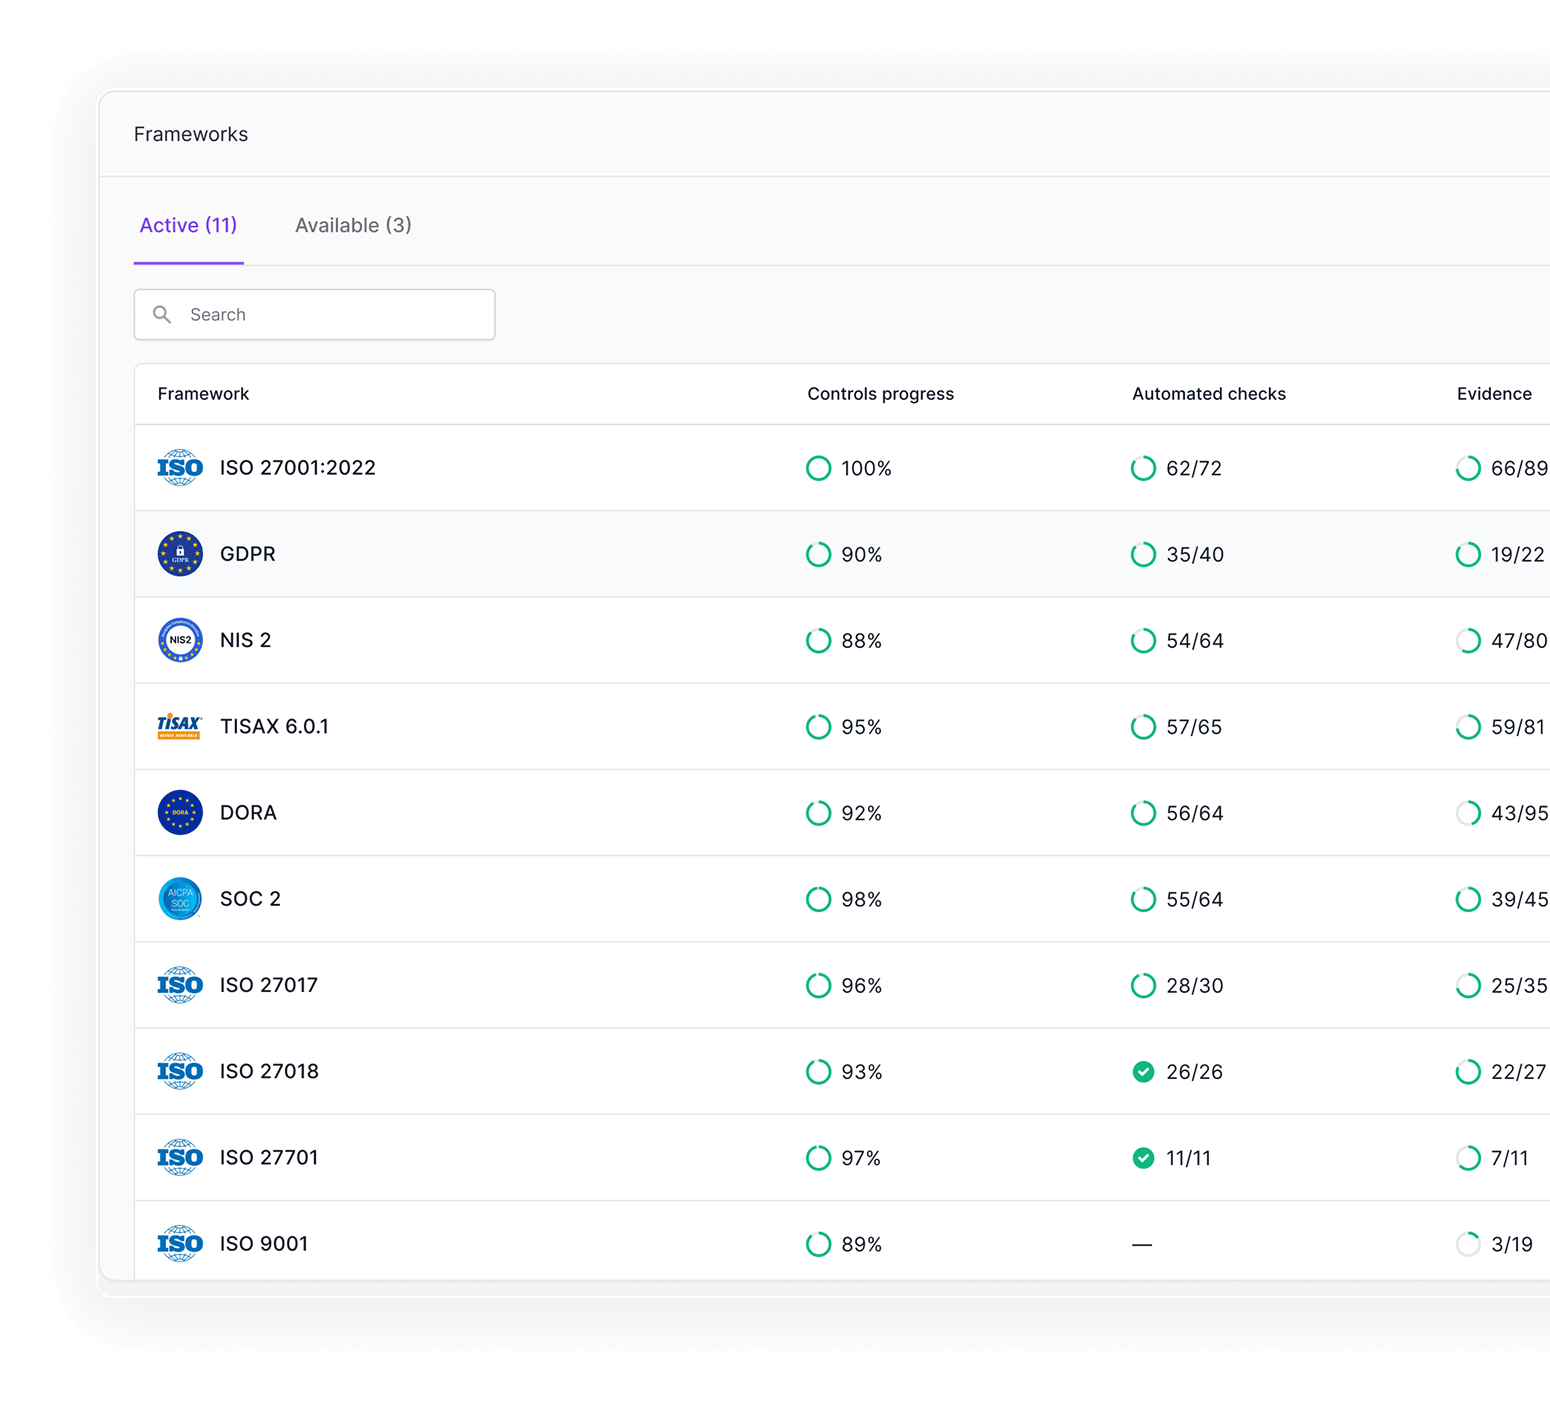
ISO 27001, NIS 2, ISO 42001, SOC 2, and more. All frameworks run in the same account on one control set. Build a control once and it satisfies every framework that asks for it, so the next standard is a gap to close rather than a project to start.
Your Statement of Applicability, risk register, and policies stay single sources of truth instead of rebuilding them for each framework.

Build one ISMS for the whole group
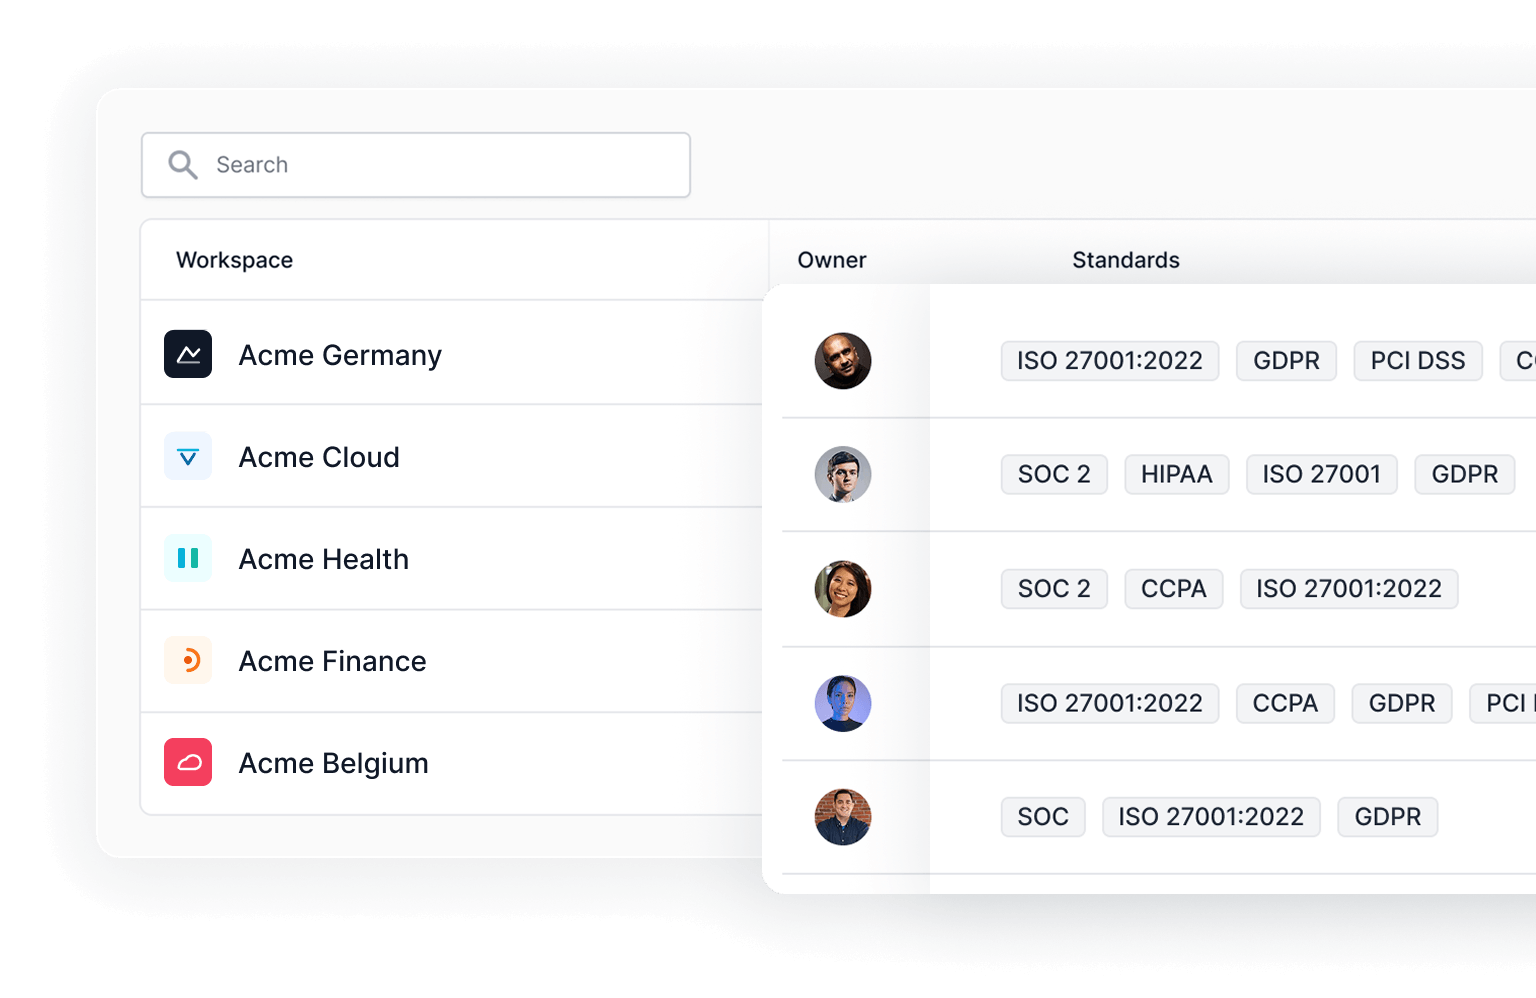
Run a distinct compliance program for each subsidiary, product, or business unit without setting up separate systems. Frameworks, controls, and evidence are scoped per workspace, while shared personnel, vendors, and assets stay central.
Every entity can use its own scope and its own auditor, while the group keeps one view across all of them.
Collaborate with everyone in one central place
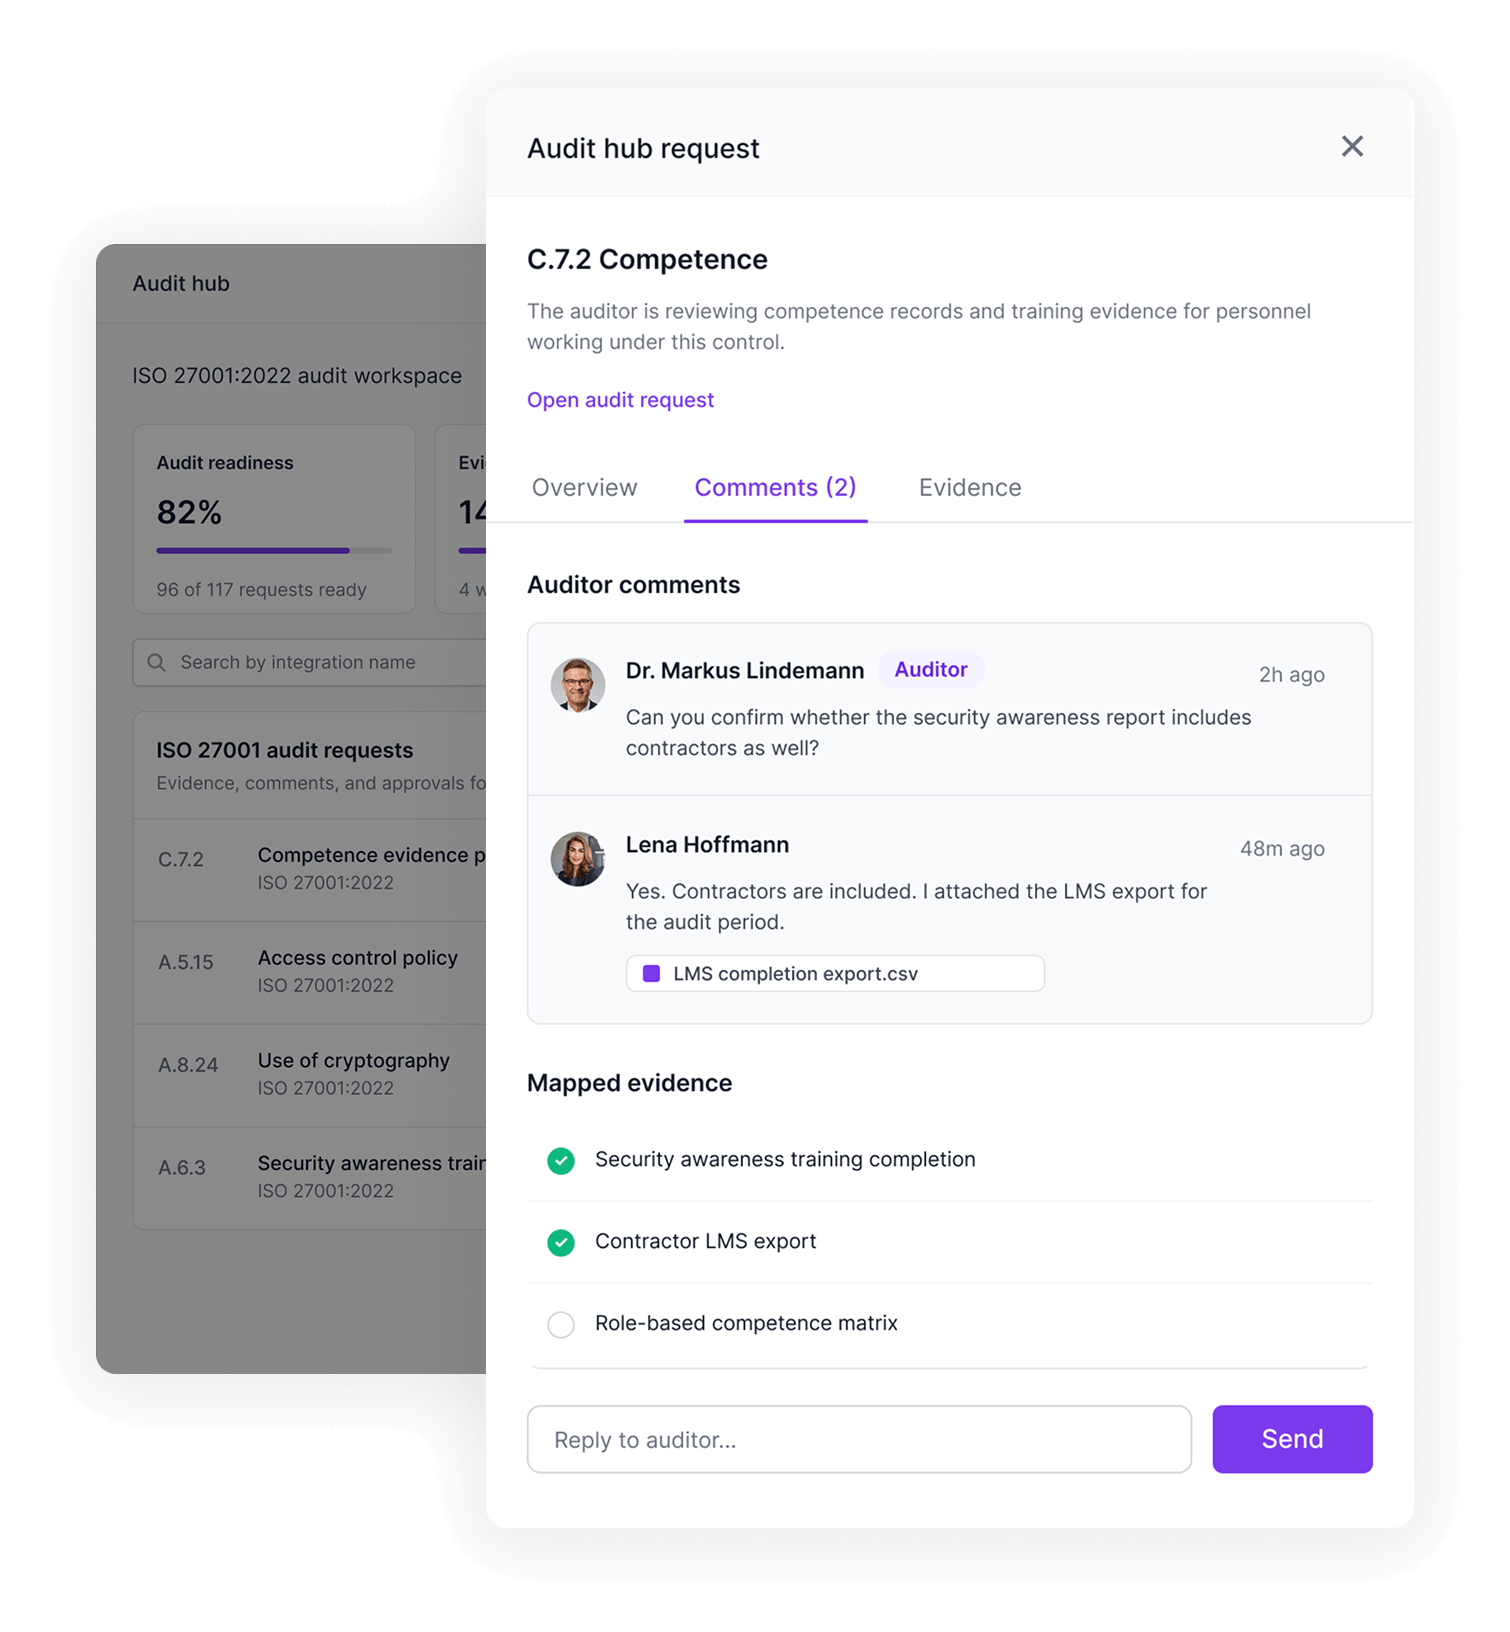
Compliance, IT, quality management, legal, HR, and management - all work in the same account with clear ownership across controls. Your auditors get structured, view-only access to the evidences via the dedicated Secfix audit-hub.
Recurring work is scheduled, assigned, and tracked, so you stay audit-ready all year instead of running a screenshot sprint before each audit.
One platform for your entire company

Manage every entity in one account, with shared controls and evidence across your company.

Get every control mapped to the right evidence, and know exactly what your auditor needs.


Replace the risk spreadsheet with a live risk register mapped to 100+ controls.

Onboard, train, and offboard your team with automated reminders and progress tracking.

Find every vendor automatically, rate them by risk, and get review reminders.

Answer buyer security questions from your own policies instead of starting over every time.
Security and IT leaders build on Secfix

“Secfix enabled us to achieve the ISO 27001 certification swiftly and efficiently, a success we could not have accomplished without them.”


Secfix combines ease of use with real audit depth. For companies that want to truly live ISO 27001 not just check the box it's the perfect platform.


The platform gave us a structure and maturity we couldn’t have achieved on our own. Without it, the process would have taken years, and success in our first audit would have been unlikely.


Secfix is more than just software—it’s a partner who could guide you through the entire process. Secfix offered the perfect combination of the right size, good value for money, and the features we actually needed.


Secfix has exceeded my expectations in every way. The process of creating security policies was a breeze. Getting ISO 27001 compliant with Secfix is a game-changer for the way that MIXMOVE is able to sell into larger companies. The Customer Success team has proven to be a valuable asset. They are so quick to answer questions, it’s very comforting knowing they’re there for us.

“I strongly recommend Secfix to any organization that wants to simplify their compliance management and stick to standards. Secfix’s easy-to-use interface, strong documentation management, and helpful reporting features have been key to our successful ISO certification. For any company looking to improve their compliance efforts and see real results, Secfix is a must-have tool.”


“The combination of an intuitive platform and knowledgeable team made Secfix the ideal partner for Tanso’s certification journey."


Secfix made what seemed like an overwhelming process incredibly smooth and efficient. Their automation and expert support were game-changers for us.


“I recommend Secfix to any company starting the journey of ISO 27001 and TISAX compliance with data protection. Their platform and dedicated support made the process much more manageable. In fact, I have already recommended Secfix to several peers in the industry.”

Secfix is rated a leader on G2
Secfix consistently ranks as a G2 industry leader based on hundreds of customer reviews.
One setup for every framework. See how it works.


FAQs
Can we run several frameworks in one ISMS?
Yes, and it is the normal case for Secfix customers in this size range. ISO 27001, NIS 2, TISAX, SOC 2, GDPR, DORA, ISO 9001, and more run in one account on a shared control set of 100+ pre-built controls. A control implemented once satisfies every framework mapped to it, and one piece of evidence is reused wherever it applies. Your Statement of Applicability, risk register, and policy set stay single sources of truth rather than forking per standard.
How does Secfix handle multiple legal entities or subsidiaries?
Each entity gets its own workspace. Frameworks, controls, monitoring, and evidence are scoped per workspace, so a subsidiary can hold a different certificate, a different scope, and a different auditor from the rest of the group. Shared policies, personnel, vendors, and assets stay central and are linked rather than duplicated. Group-level dashboards show audit readiness and control performance across every entity, while events and test results stay filterable per workspace.
Who can work in the platform, and can our auditor and DPO have access?
Everyone who touches compliance, with permissions per role: IT, your information security officer, quality management, legal, HR, management, and more. External parties work in it too. Your data protection officer gets their own access, and external auditors get structured, view-only access via our audit hub to the exact evidence, policies, and controls they need to sample, rather than being sent folders of exported screenshots.
Is Secfix a European platform, and where is our data hosted?
Yes. Secfix is built in Germany, headquartered in Munich, and customer data is hosted in the EU by default. Support and the in-house compliance experts are European too, with ISO 27001, NIS 2, and TISAX as core competence rather than catalogue entries. It is a different starting point from a US platform that added EU hosting as an option later.
Does NIS 2 apply to us?
It depends on your sector and your size. NIS 2 covers a defined list of essential and important sectors, and national implementations vary across EU member states, so the answer depends on where your entities are registered as much as what you do. Many mid-market companies also encounter it indirectly, because a customer inside scope passes requirements down the supply chain. NIS 2 is a core competence at Secfix rather than a catalogue entry, and it is mapped to your existing ISO 27001 controls.
How do we keep the ISMS alive between audits?
Evidence collects continuously, and every recurring obligation is scheduled, assigned, and tracked: policy reviews, access reviews, vendor reviews, management review, internal audit. Owners are notified before things fall due rather than after. The intent is that you stay audit-ready all year instead of reconstructing a year of evidence in the weeks before each audit.
We already have an ISMS in spreadsheets or another tool. Can we move it?
Yes, and most mid-market customers arrive with something in place. Existing policies, risk registers, and evidence come across and get mapped onto the Secfix control set, so the work already done is not repeated.
What does compliance cost at our size?
The Secfix subscription depends on your scope, your technical setup, and how many entities you run. The audit itself is billed separately by your certification body and scales with headcount and scope. Because certification runs on a three-year cycle with annual surveillance audits, it is best budgeted as an ongoing program rather than a one-off purchase.
Build one compliance system that lasts
Talk to a Secfix expert to map your frameworks, your entities, and your stakeholders onto a single setup.