
Security compliance for startups
Secfix takes you from 0% to 100% compliant, automates up to 90% of your manual work, and opens the deals you are building toward.
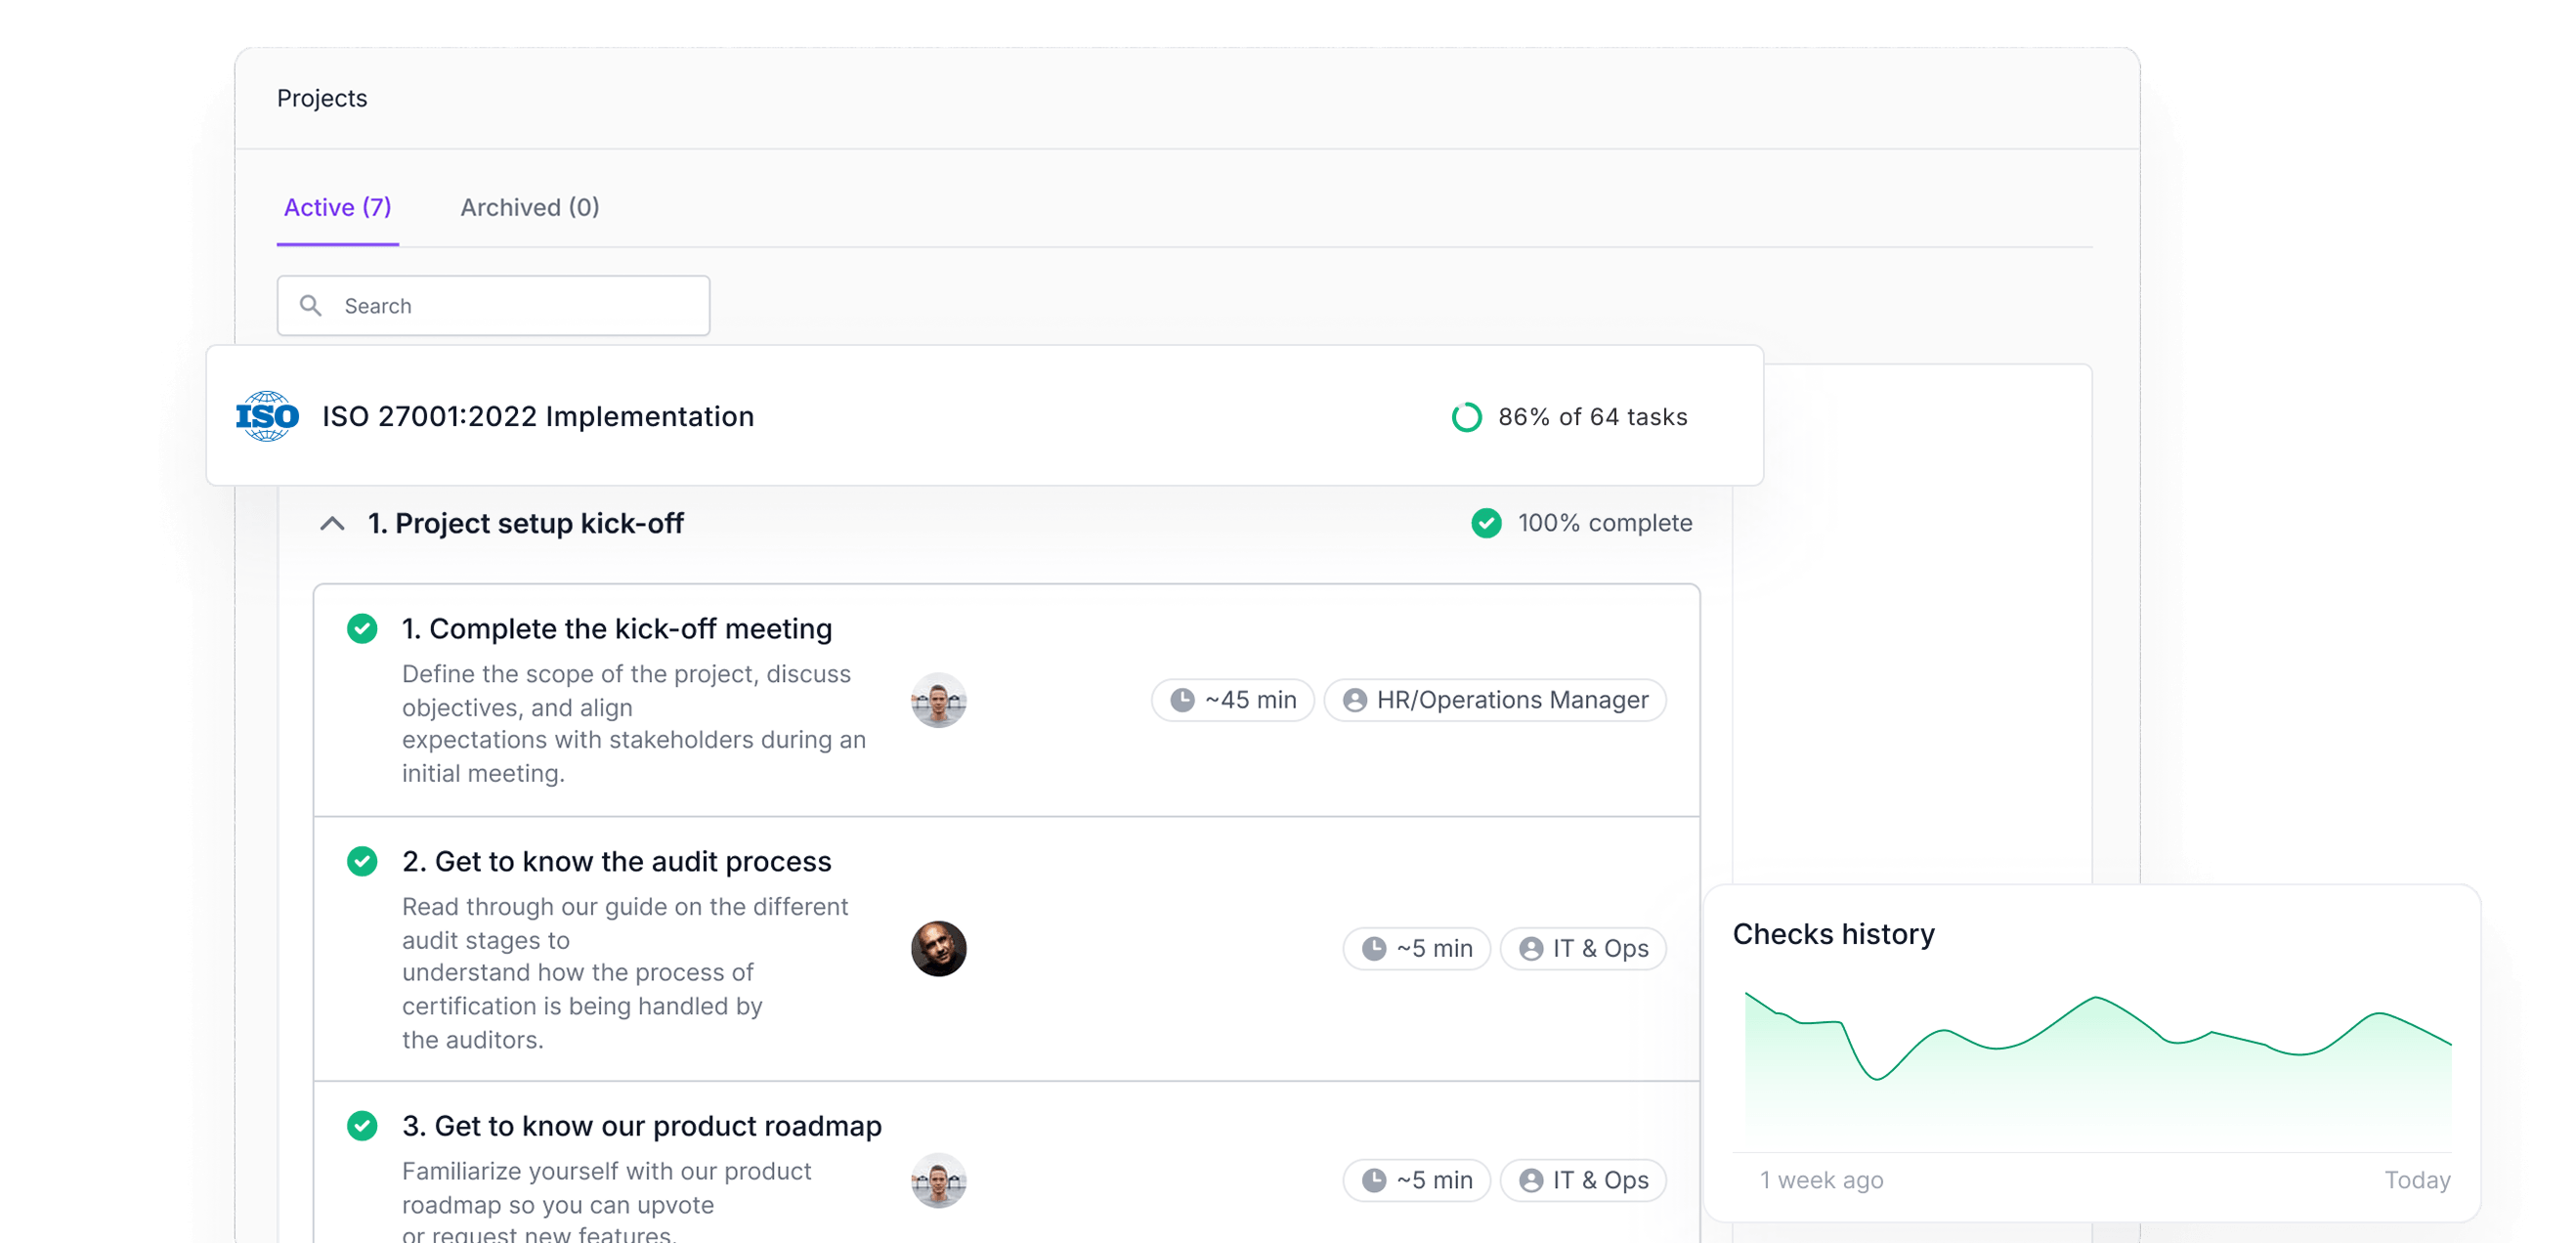



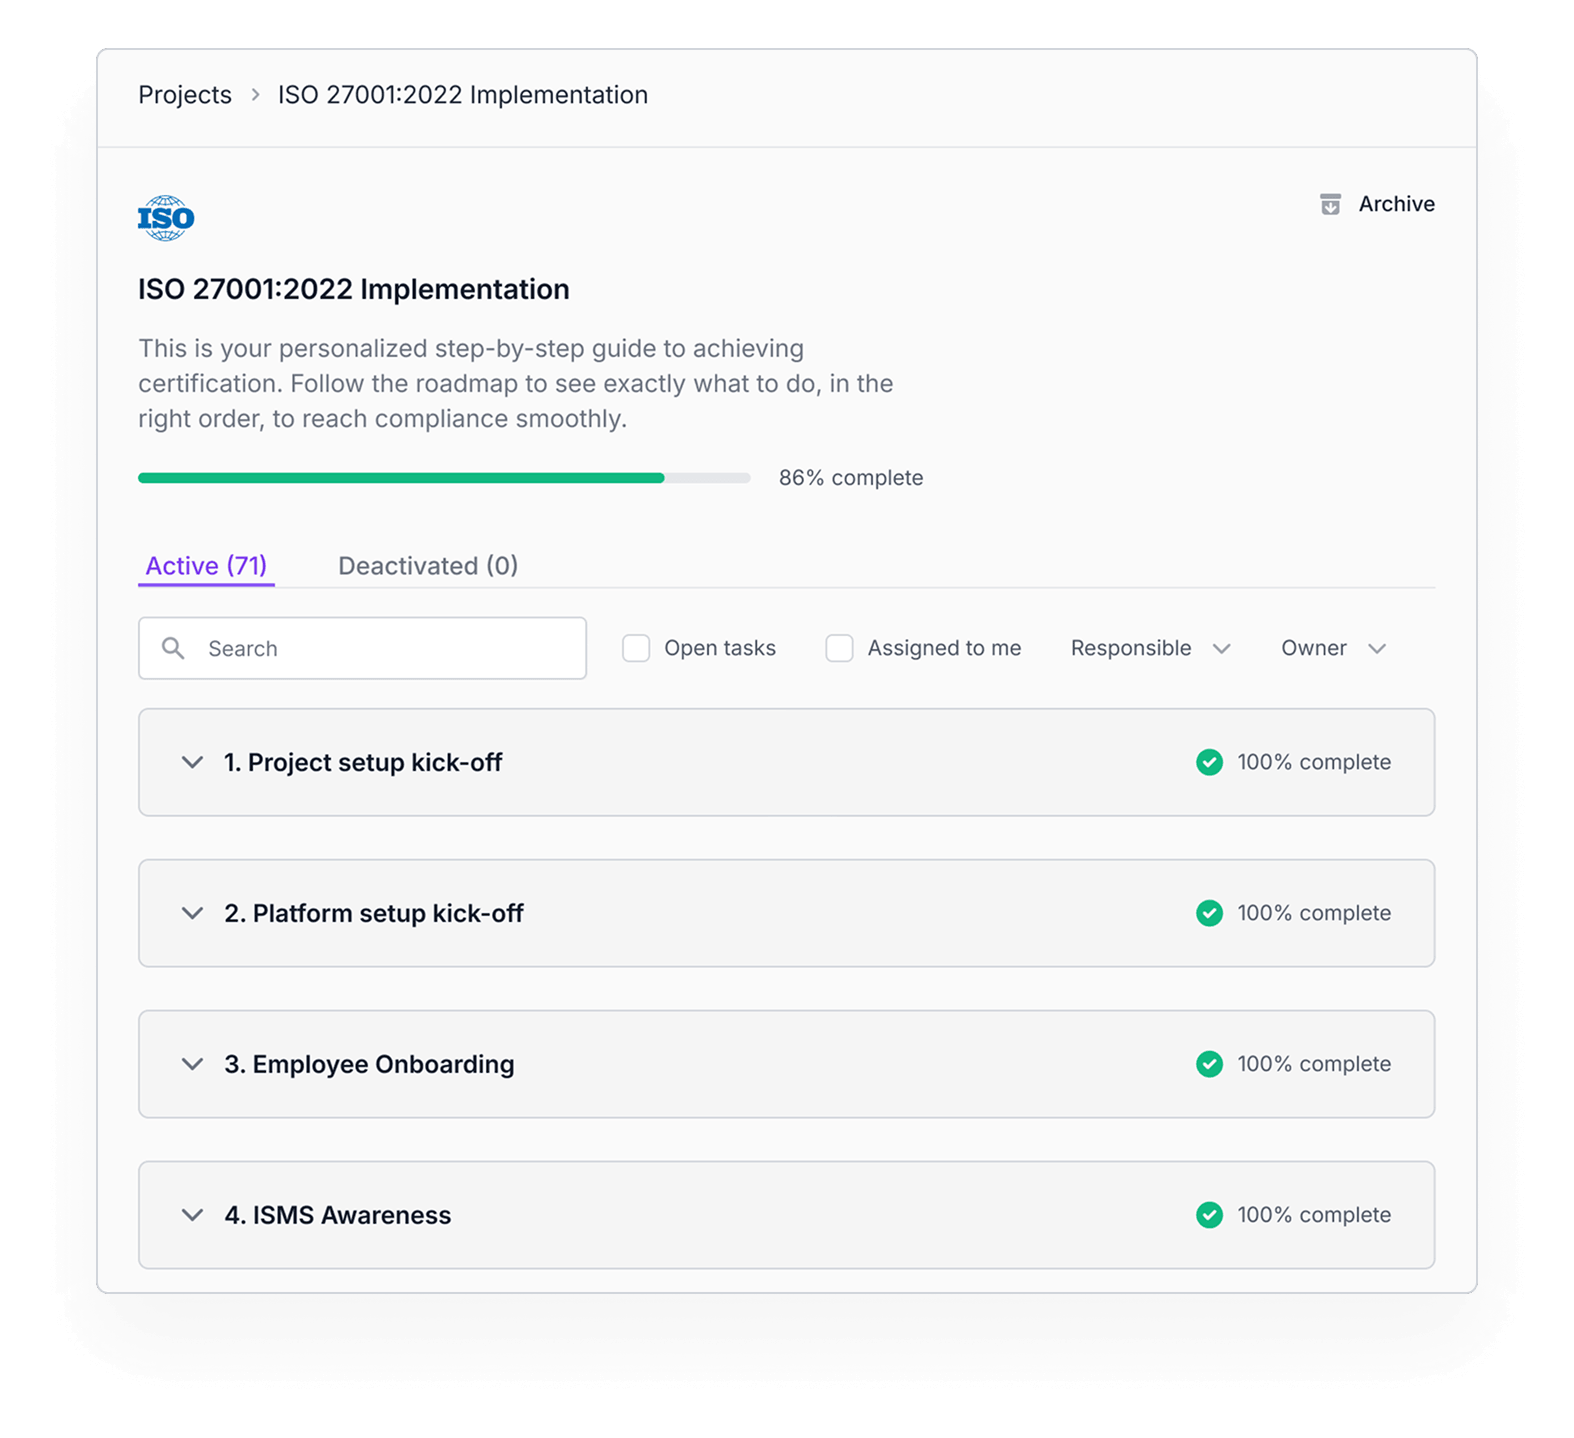
No compliance experience needed. Just follow the plan.
Secfix gives you the full project plan: gap assessment, implementation, internal audit, external audit, then maintenance. Every phase shows what happens next and who owns it, so you are never guessing what to do on Monday morning.
Evidence collects itself through 100+ integrations, and auditor-approved templates mean nobody starts from a blank page. No compliance hire required.

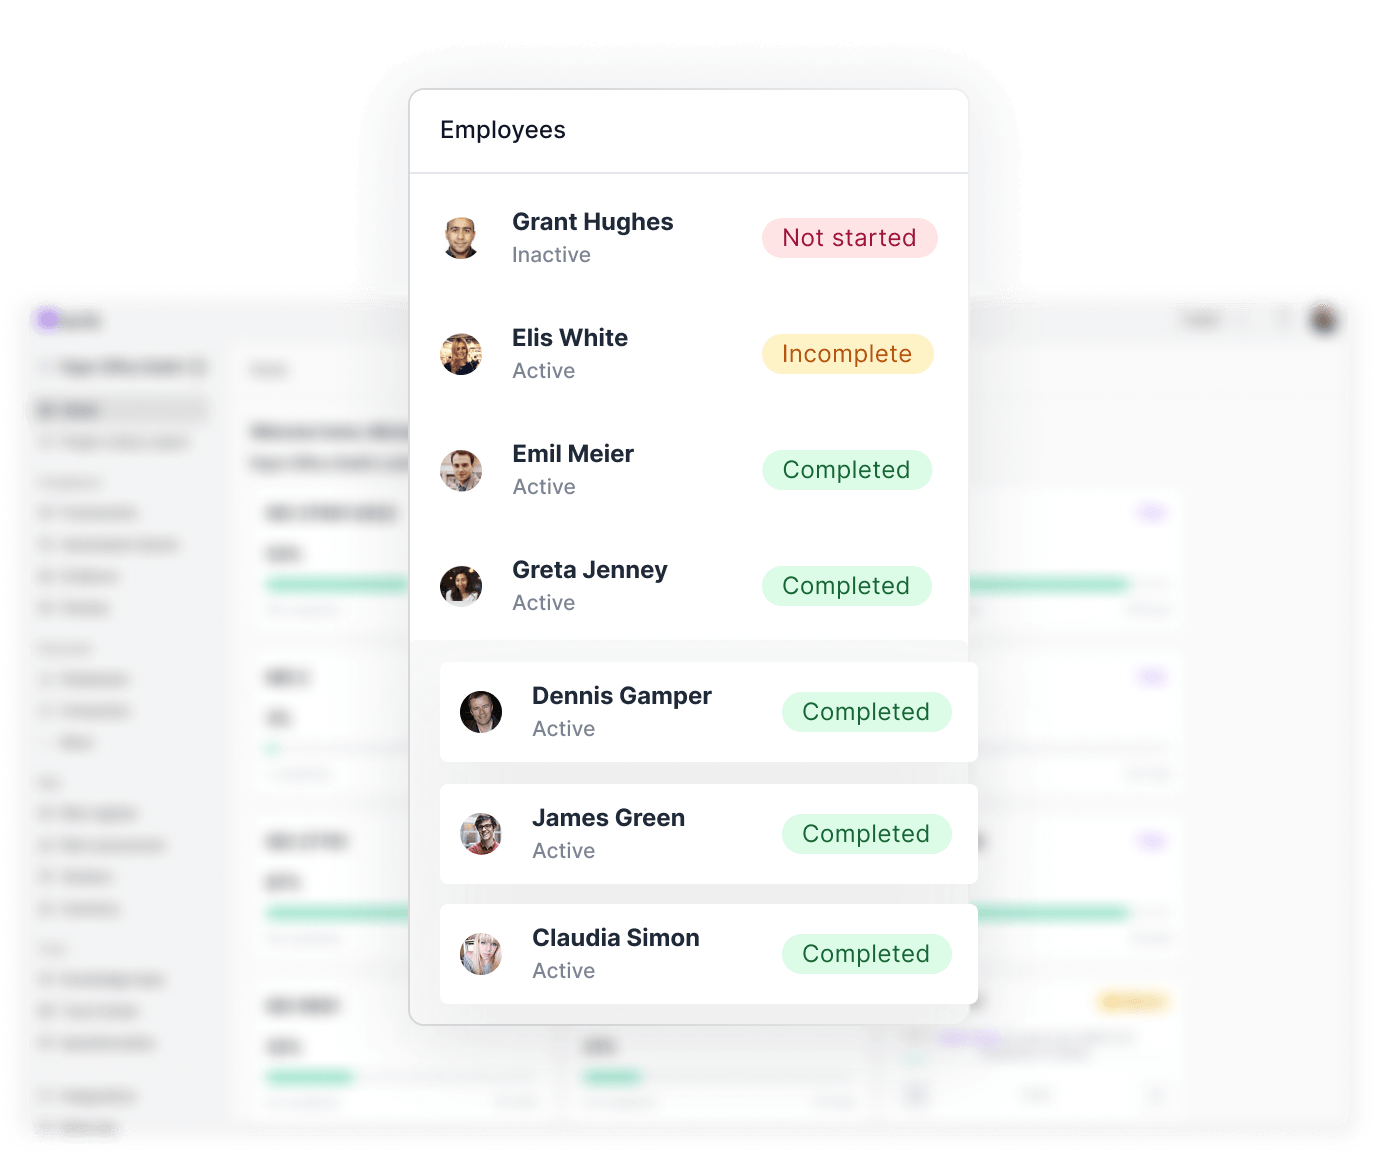
Grow the team. Add the standards your buyer asks for.
Hire as fast as you want, because your compliance work does not grow with your team size. New joiners get their policies, security training, and platform access on day one. Every new laptop can be checked the moment it arrives.
Your buyers and regulators rarely stop at one standard. Whether the second one is ISO 27001, SOC 2, or NIS 2, your controls already carry across.
Your next buyer asks tomorrow. Answer them today.
From the day you kick off, you can publish your Trust Center on your own website with your progress and a signed Letter of Attestation. This means prospects can run their full security review before your certificate exists and your pipeline doesn’t get blocked by compliance.
When a buyer sends a security questionnaire, Secfix drafts the answers from your own policies instead of you starting over each time.

Everything SMBs need to master security compliance

Connect your cloud, identity provider, and business tools so evidence starts collecting itself.


Check encryption, screen lock, antivirus, and passoword manager on every laptop. No MDM needed.

Get every control mapped to the right evidence, and know exactly what your auditor needs.

Onboard, train, and offboard your team with automated reminders and progress tracking.

Publish certifications, policies, and a signed Letter of Attestation on your website.

Ask anything about your ISMS and get answers sourced from your evidence and documentation.

Answer buyer security questions from your own policies instead of starting over every time.
Hundreds of startups build on Secfix

“I strongly recommend Secfix to any organization that wants to simplify their compliance management and stick to standards. Secfix’s easy-to-use interface, strong documentation management, and helpful reporting features have been key to our successful ISO certification. For any company looking to improve their compliance efforts and see real results, Secfix is a must-have tool.”


“The combination of an intuitive platform and knowledgeable team made Secfix the ideal partner for Tanso’s certification journey."


“I’d recommend Secfix in a heartbeat. Secfix made our journey to ISO 27001 certification seamless and fast. "


“I recommend Secfix to any company starting the journey of ISO 27001 and TISAX compliance with data protection. Their platform and dedicated support made the process much more manageable. In fact, I have already recommended Secfix to several peers in the industry.”


Secfix saved us an enormous amount of time and effort. Everything was pre-filled and well-structured. We no longer had to scramble to find documentation - it was all there, clearly organized.


Secfix made what seemed like an overwhelming process incredibly smooth and efficient. Their automation and expert support were game-changers for us.

Secfix is rated a leader on G2
Secfix consistently ranks as a G2 industry leader based on hundreds of customer reviews.
Everything SMBs need to master security compliance


FAQs
Which compliance framework does a startup need first?
The one your buyers are asking for. ISO 27001 is the framework most Secfix startup customers certify first, because it is what European mid-market and enterprise procurement and investors ask to see. SOC 2 comes first when your pipeline is mostly US companies. Because Secfix cross-maps every control, the second framework is a delta on the first rather than a fresh start.
Do startups really need ISO 27001?
It is not legally mandatory in most countries, but it is often commercially mandatory. Startups typically start when procurement says they will sign once the company is ISO 27001 certified, when they are filtered out of RFPs, or when an investor raises it in diligence. If none of those has happened yet, it is a question of when, not if.
Can you get compliant without a CISO or a compliance manager?
Yes. Most Secfix startup customers have neither. The platform sequences the work and a dedicated Customer Success Manager guides you throughout the process. For teams that want someone to own security outright, Secfix offers an extended support program.
How much does compliance cost for a startup?
The price for the Secfix subscription depends highly on your technical set up and your scope. The audit itself is billed separately by the certification body, and that fee scales with your headcount and scope. Compliance is an ongoing commitment rather than a one-off purchase, so budget for annual surveillance audits and for maintaining the ISMS afterwards.
How long does ISO 27001 take for a startup?
It depends on your scope, how many controls you already have in place, and how quickly your team reviews policies and provides evidence. Manual implementation with a consultant takes considerably longer than a compliance automation platform. For verified examples: Orianda achieved ISO 27001 certification in 4 weeks with Secfix, and Tanso in 3 months.
Do you need an MDM to pass the audit?
No. Auditors need evidence that company devices are encrypted, locked, and protected, not evidence that you bought a specific tool. The Secfix agent installs on Mac, Windows, and Linux laptops and checks disk encryption, screen lock, password manager, and antivirus continuously. That satisfies the control without an MDM purchase.
Can a startup prove security before the ISO 27001 certification is complete?
Yes, and it is usually what moves a stalled deal. From kickoff, Secfix customers can publish a Trust Center on their own website showing live compliance progress and a signed Letter of Attestation from Secfix. Prospects request access, see real evidence, and often proceed with the contract before the ISO 27001 certificate is issued.
Get compliant before it costs you a deal
Connect your stack, let the evidence collect itself, and stay focused on scaling your business.